
Your extended security team, built around your business.
The MSSP that treats your business like a partner, not a ticket. Full-stack SIEM, EDR, vulnerability management, and security awareness, run by a consistent team that knows your environment.
Threats don't sleep.
Neither do we.


we usually beat it
reach your team
reclaimed annually
The present (and future) of SecOps
Cookie-cutter security doesn't cut it anymore.
What's at stake
Account team
Detection rules
Alert handling
IR costs
Compliance
Reporting
Without OneAxiom

With OneAxiom

What we deliver
Every layer managed, by analysts who know your environment.
The full stack, run for you: SIEM, EDR, vulnerability management, and security awareness. One partner, one contract. Nothing else to procure, configure, or staff.
Professional Services

SIEM
Centralized log monitoring

EDR & Vulnerability
Endpoint defense, patched fast

Security Awareness
Your team, trained to spot risk
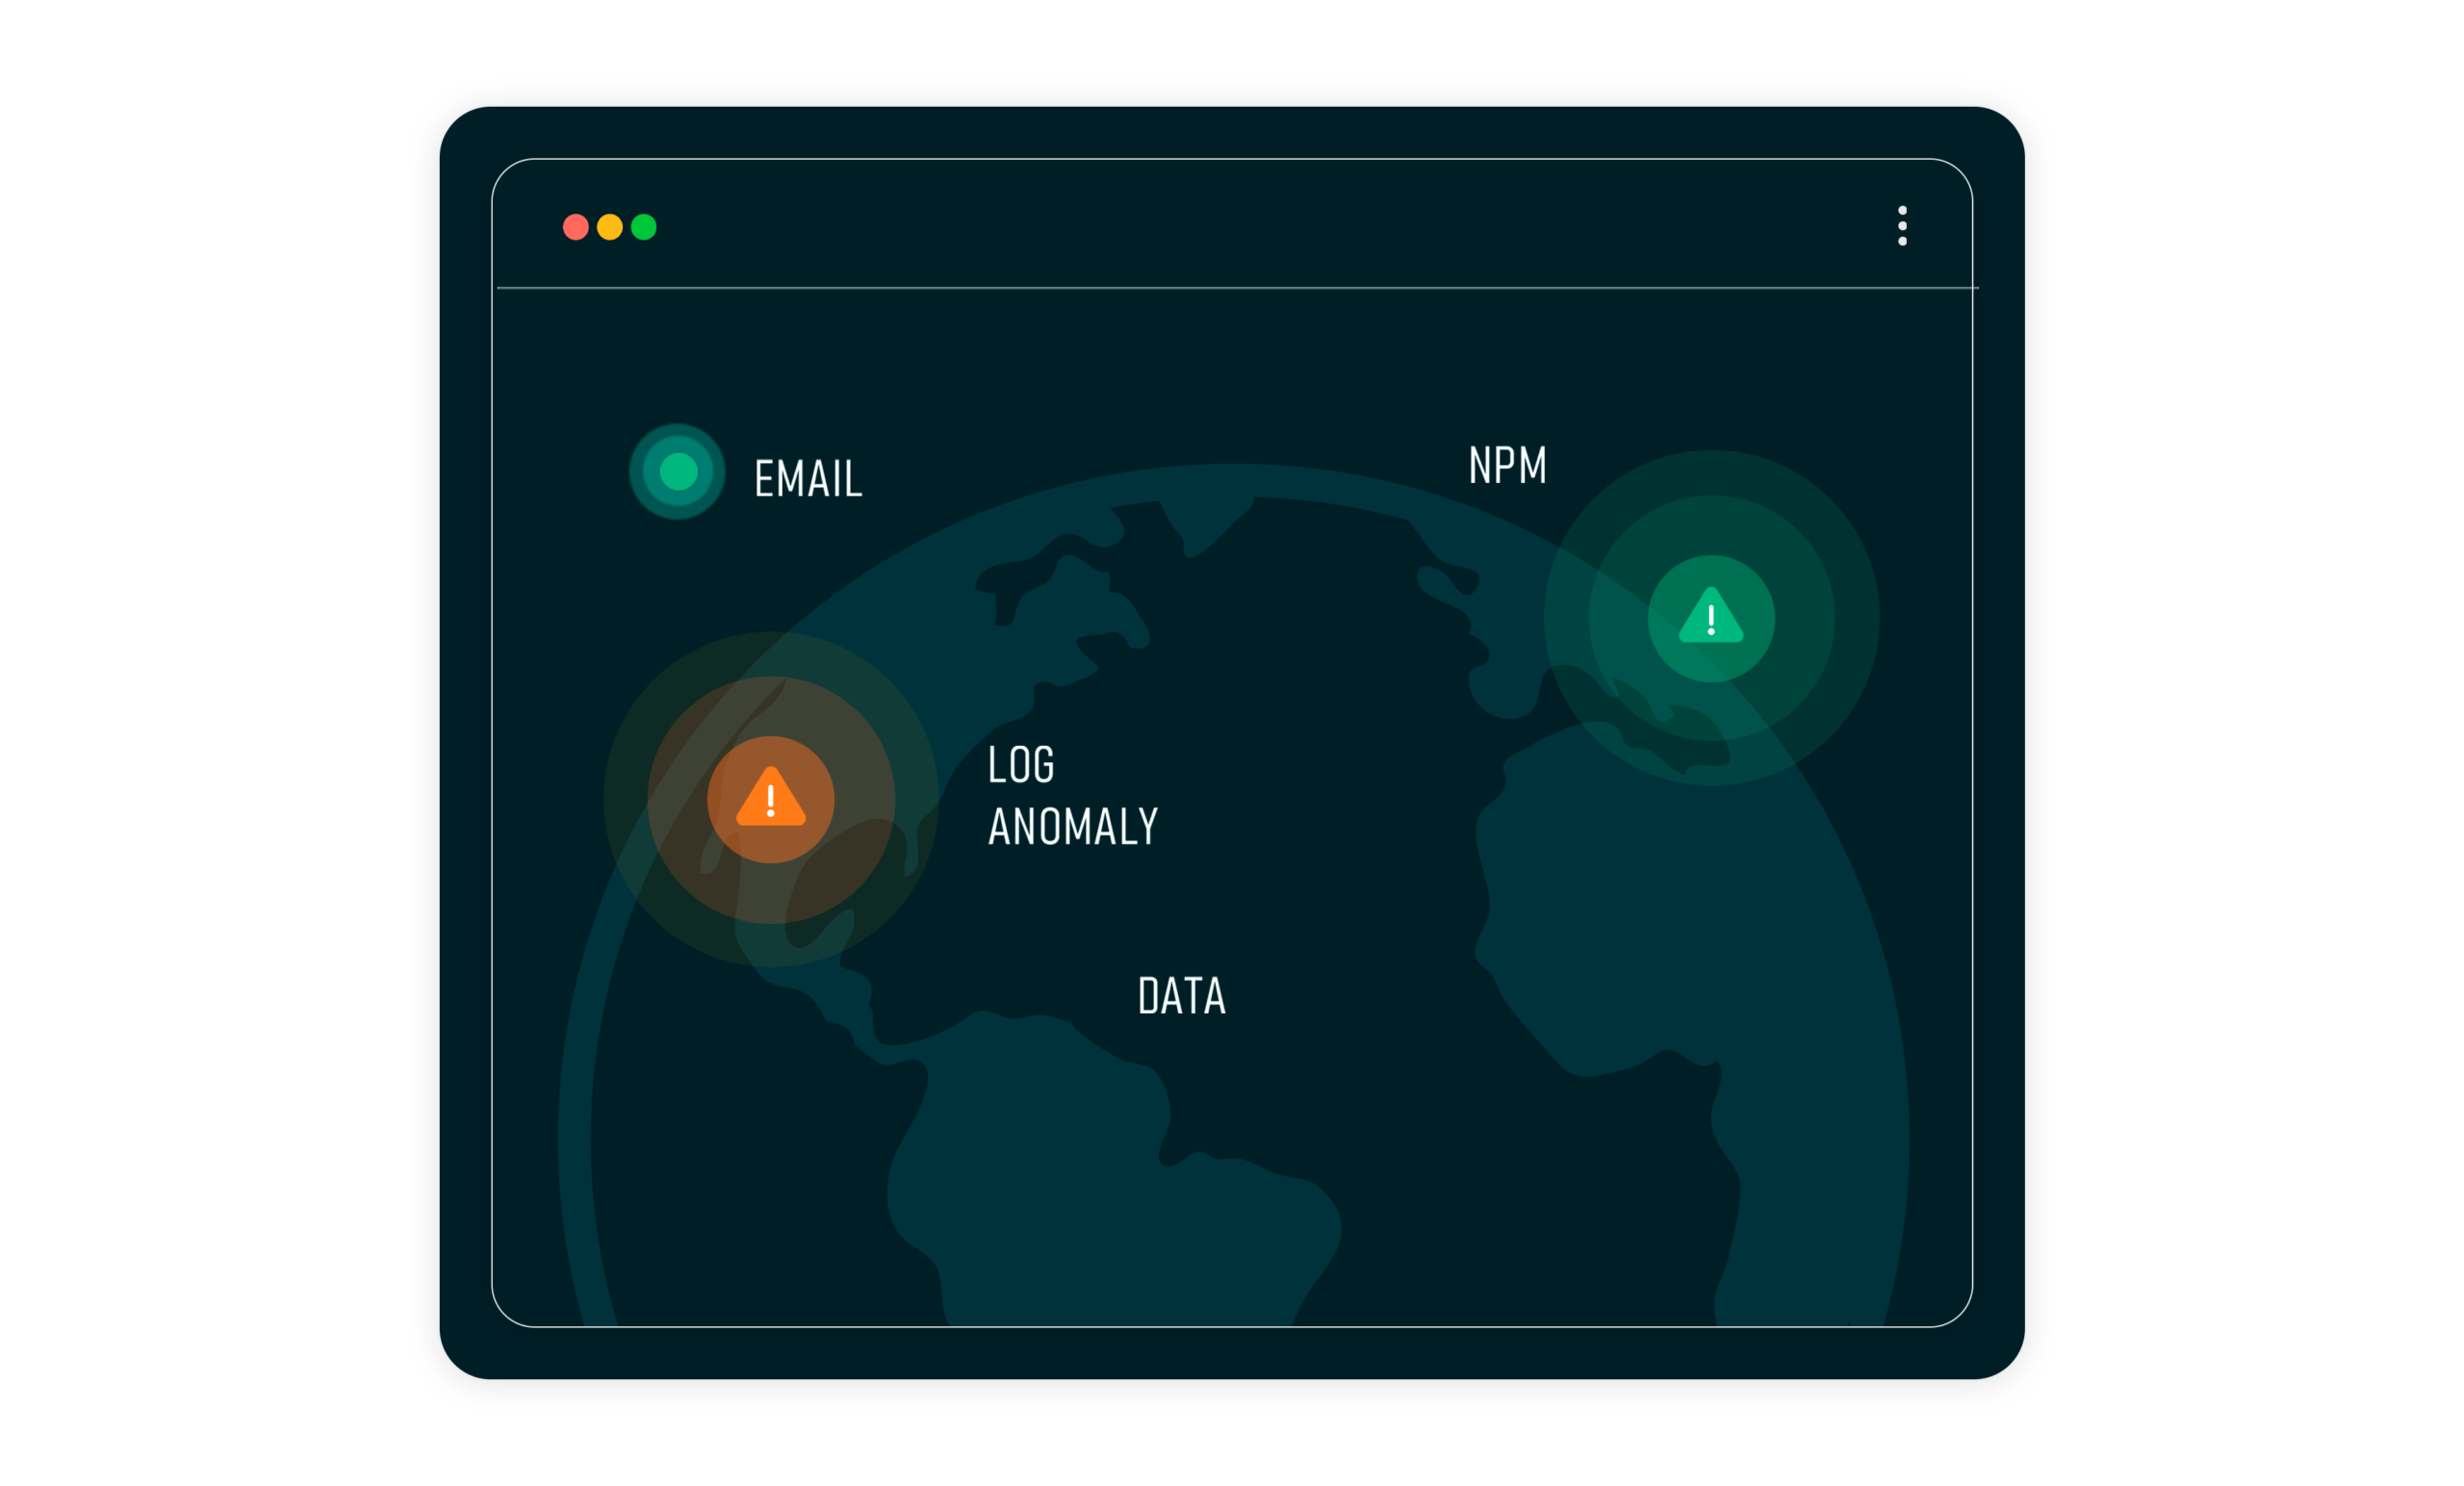
Always-on coverage
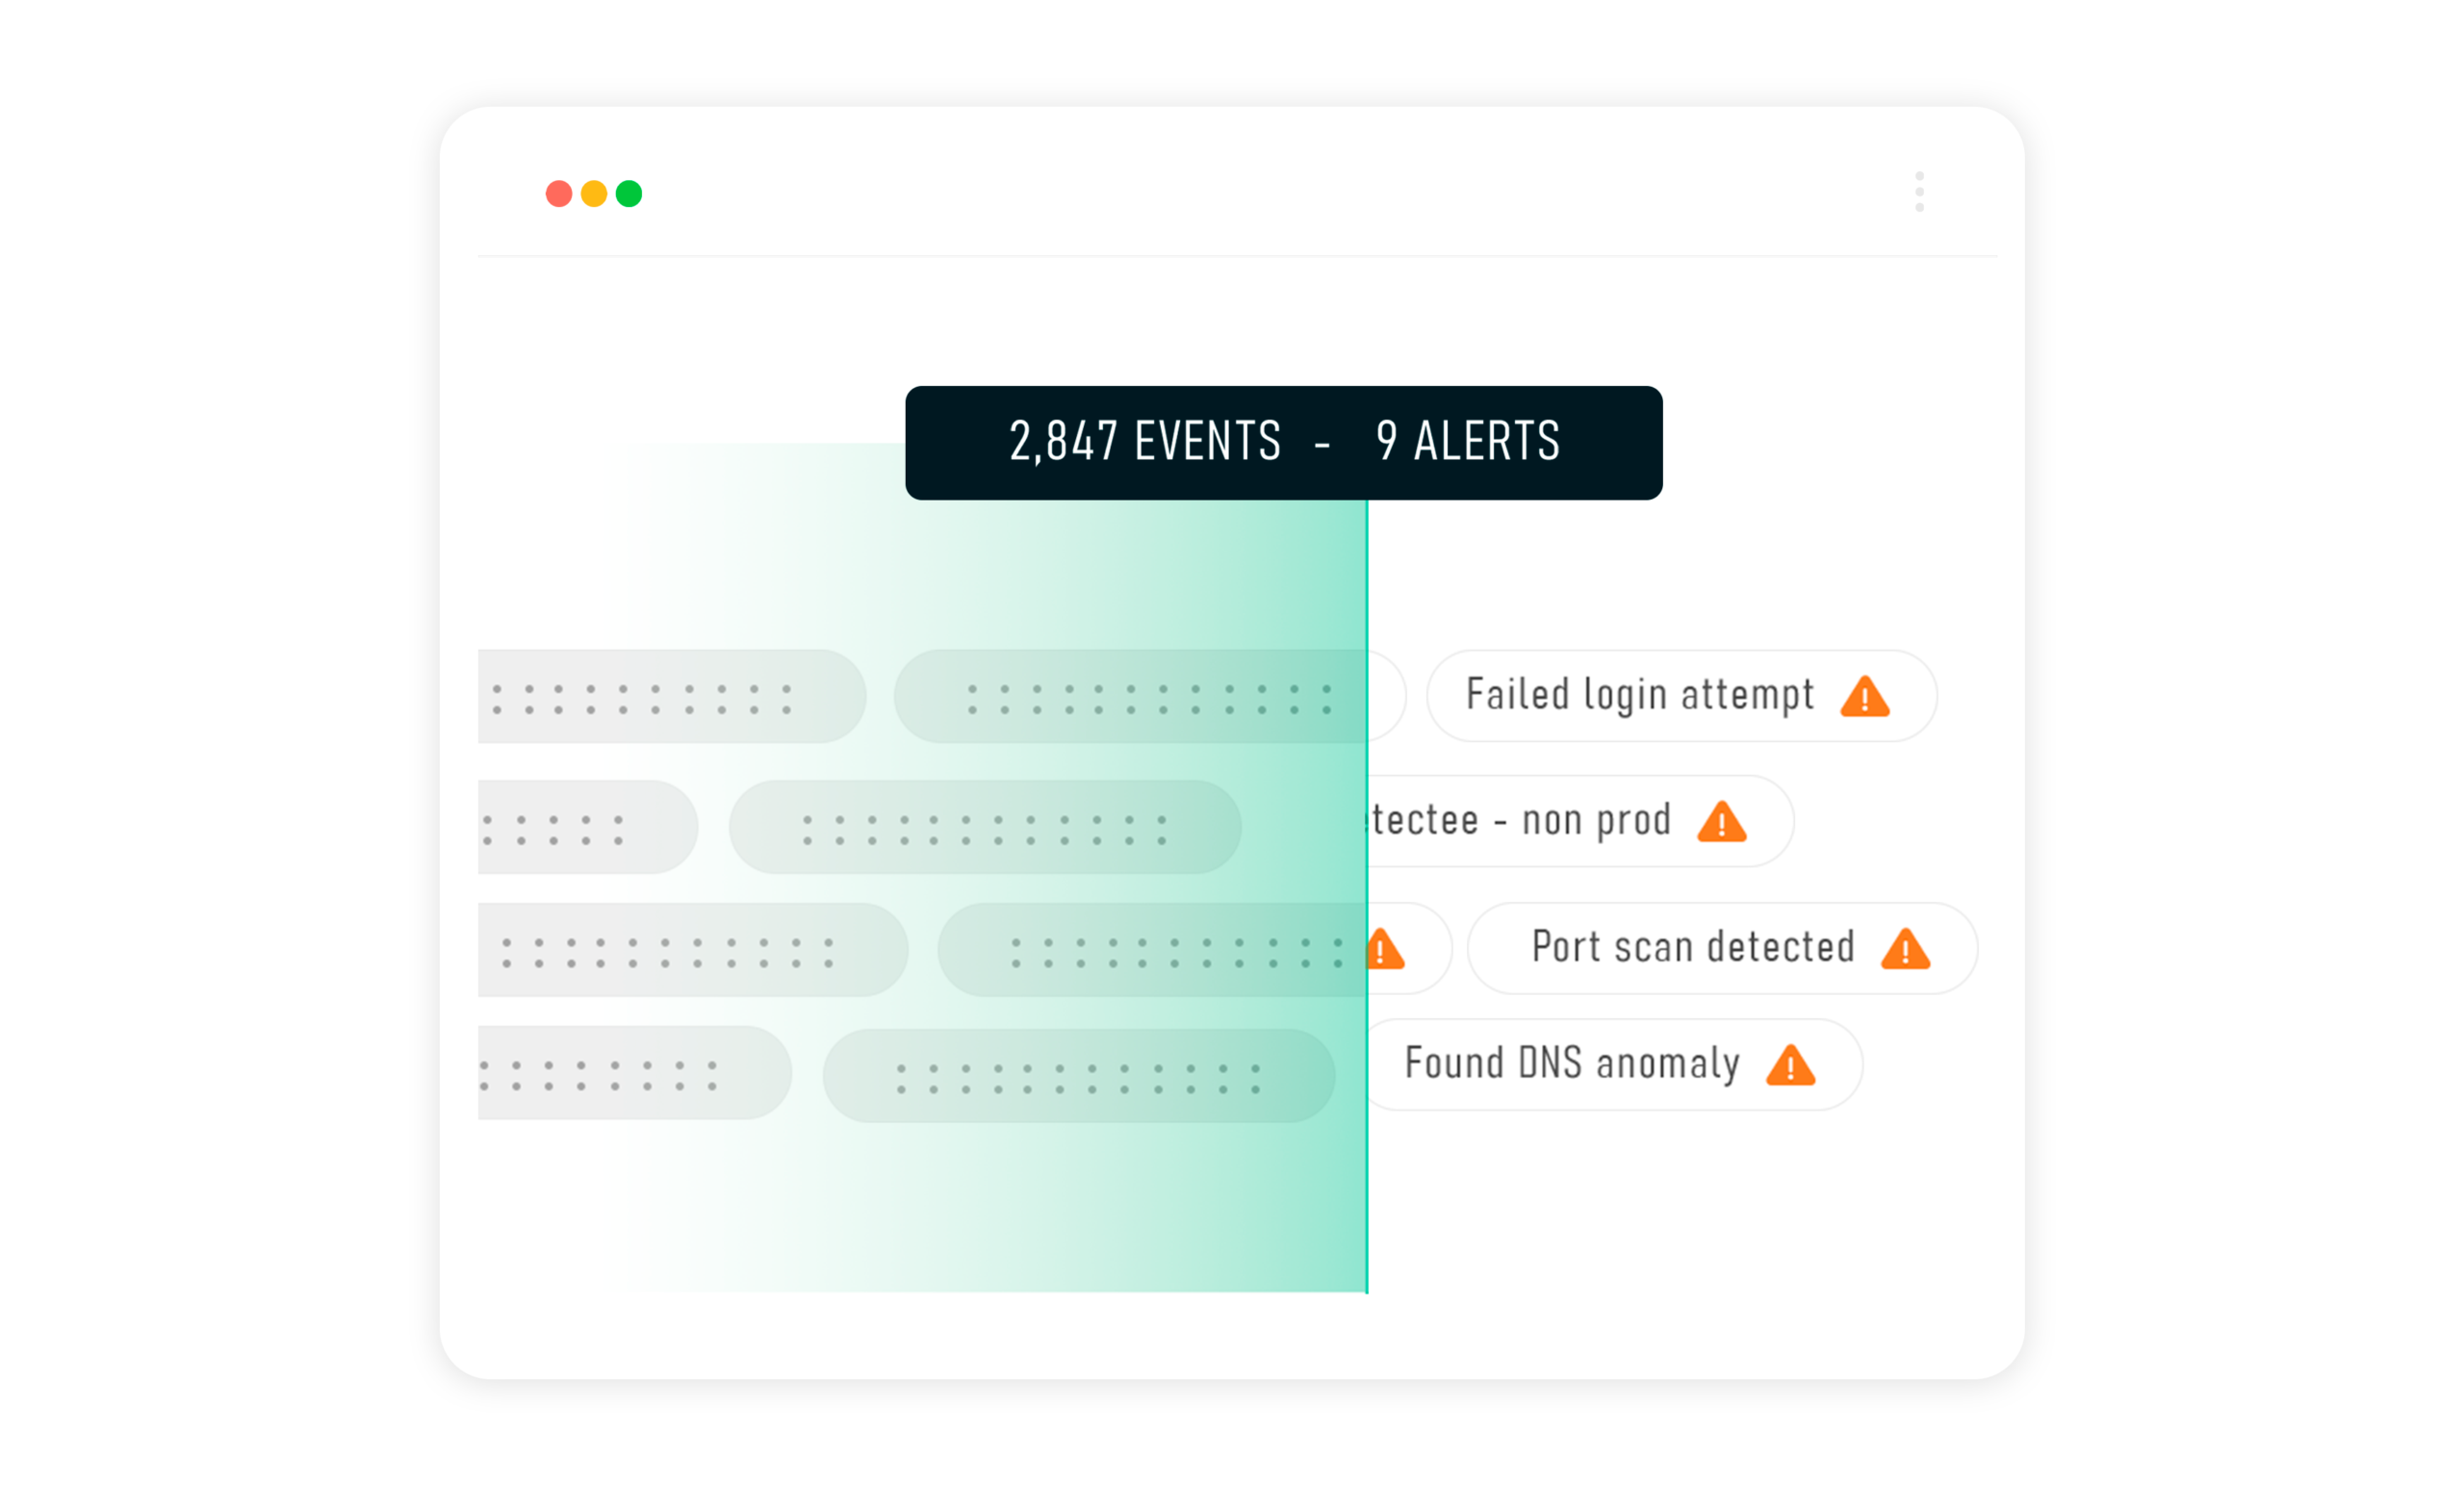
No alert noise
Security awareness

Managed SIEM
2,800+ active detection rules across our SIEM. Every alert reviewed by a person, not just a rule.

Managed EDR
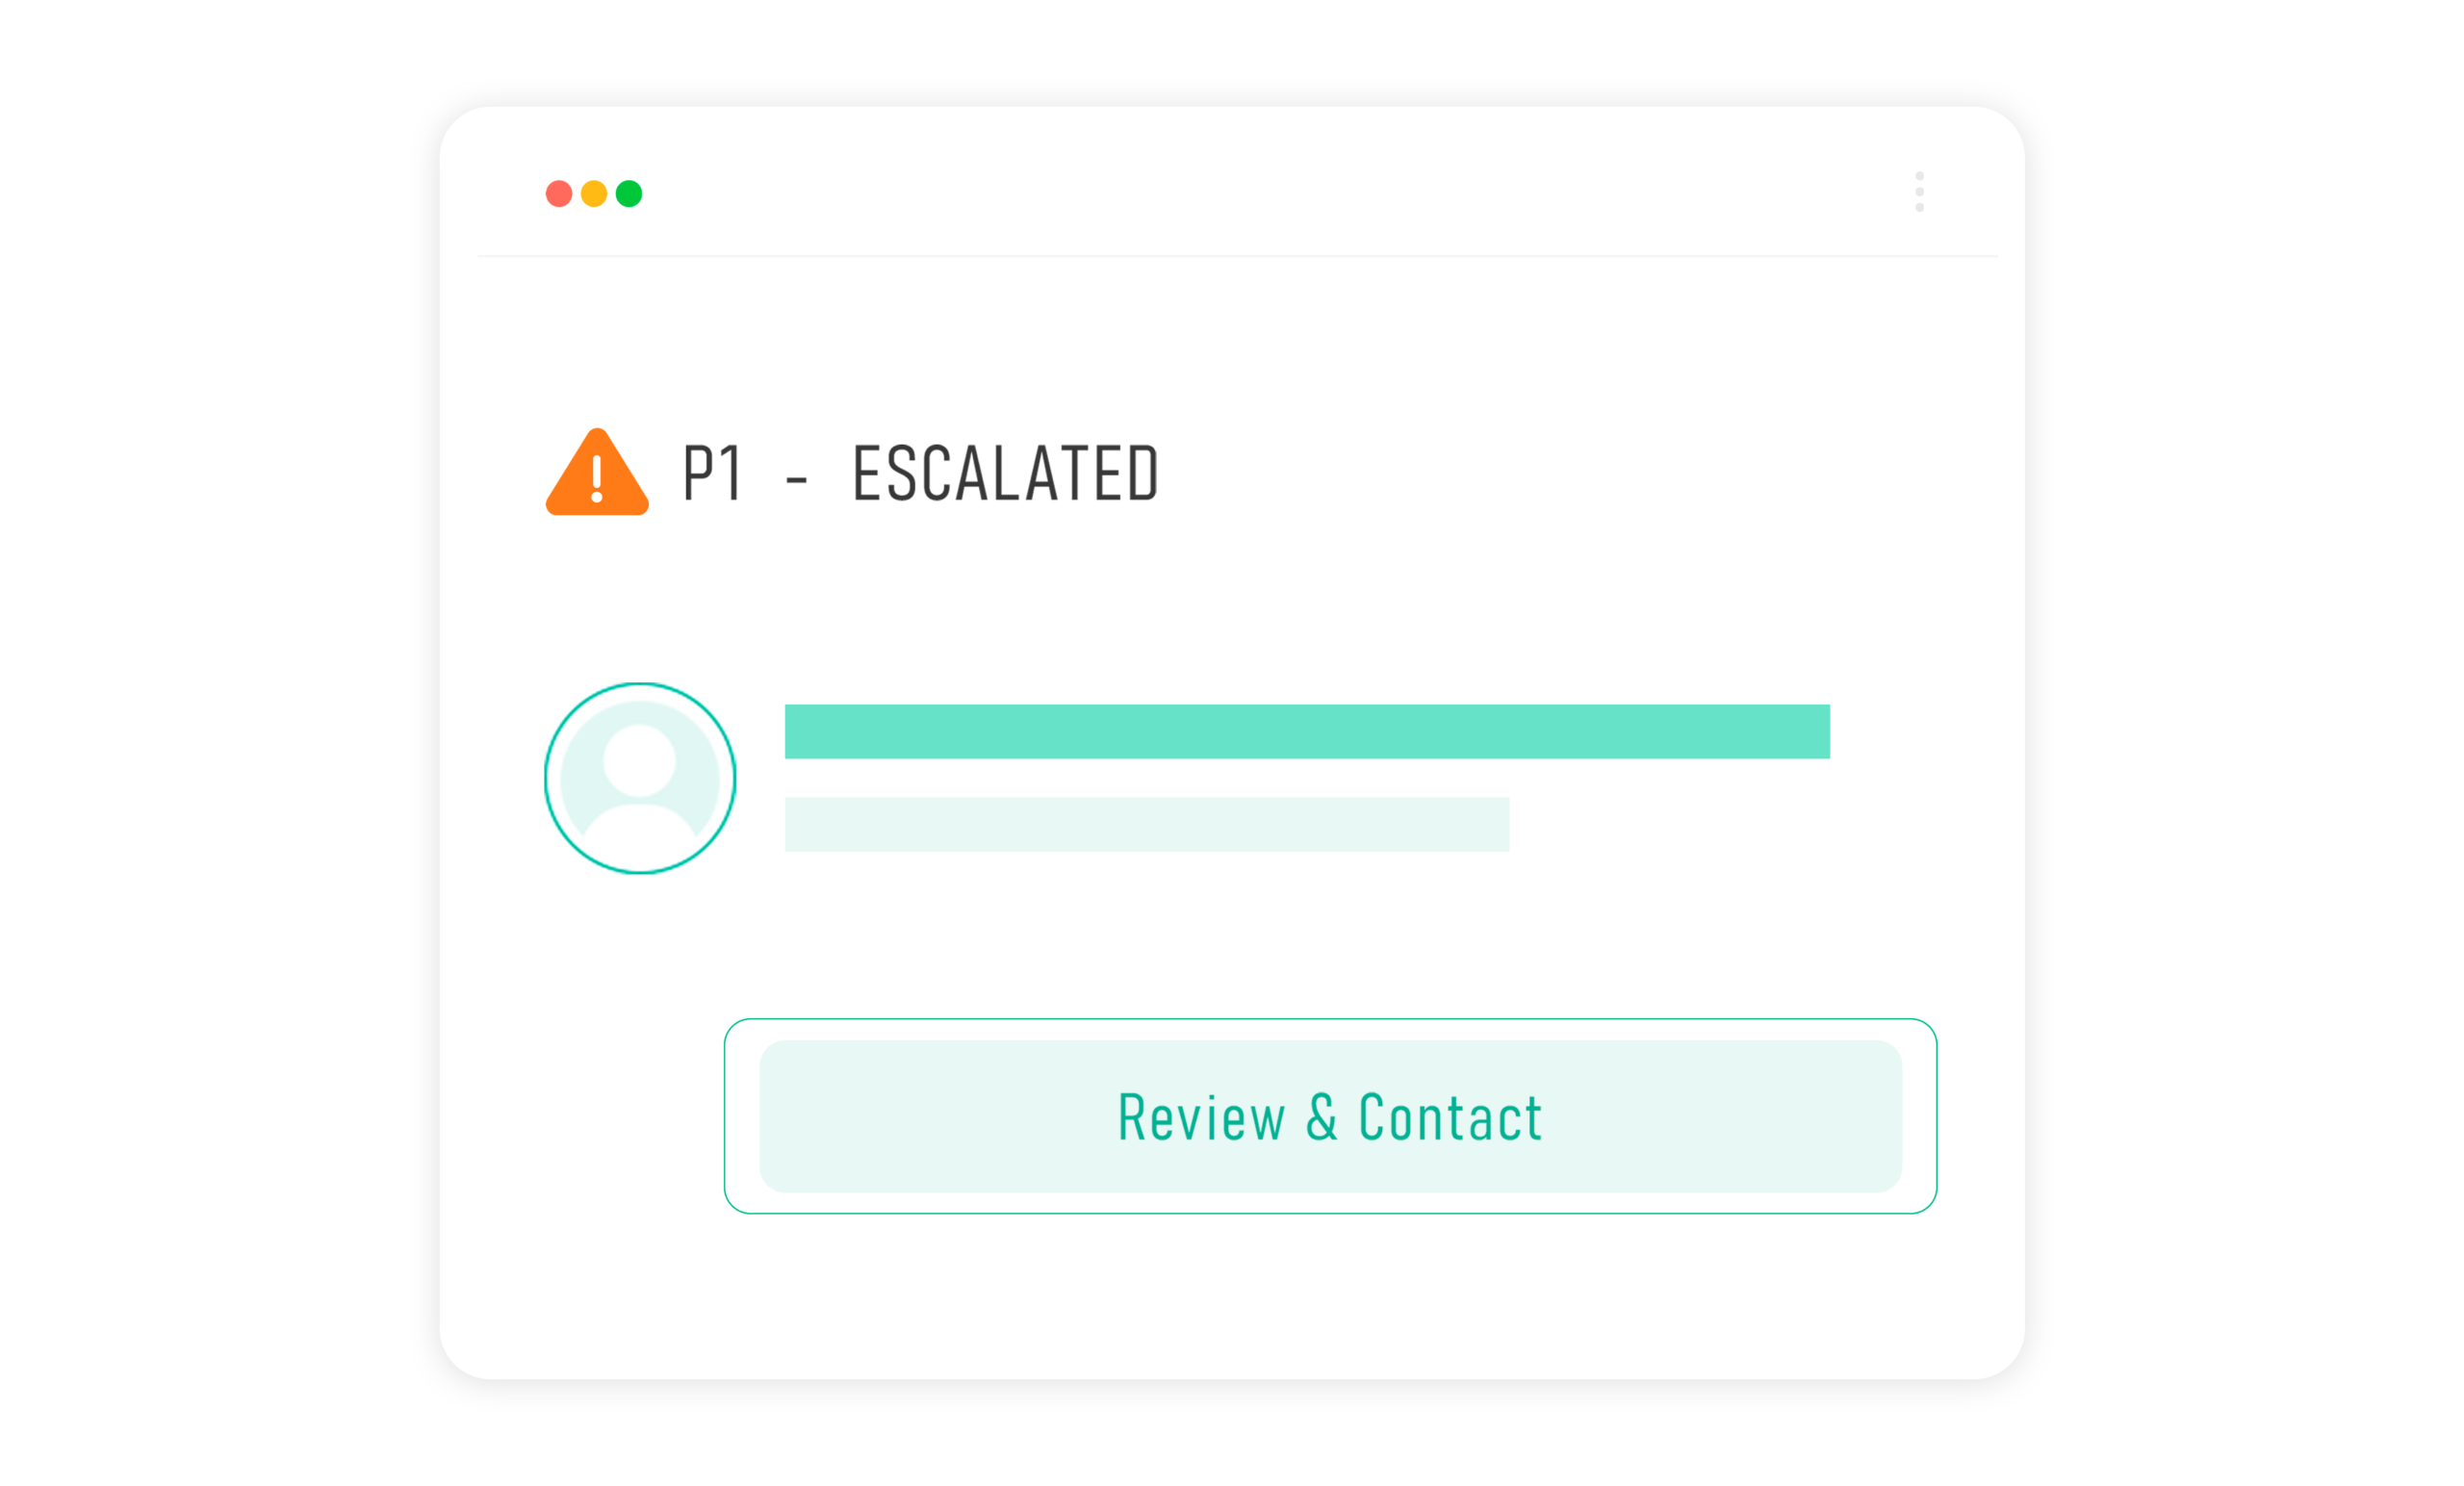
24/7 monitoring by the analyst who tuned your detection. IR included, no separate retainer.
Vulnerability Management
Every finding checked against live exploits, not just CVSS scores. Unpatched CVEs trigger SIEM detection.
Security Awareness
Phishing simulations built from TTPs active against your sector. Training fires at the point of failure, not just once a year.
What we deliver
Every layer managed, by analysts who know your environment.
The full stack, run for you: SIEM, EDR, vulnerability management, and security awareness. One partner, one contract. Nothing else to procure, configure, or staff.
SIEM
Centralized log monitoring
EDR & Vulnerability
Endpoint defense, patched fast
Security Awareness
Your team, trained to spot risk
Always-on coverage
No alert noise
Security awareness

Managed SIEM
2,800+ active detection rules across our SIEM. Every alert reviewed by a person, not just a rule.

Managed EDR
24/7 monitoring by the analyst who wrote your rules. IR included, no separate retainer.
Vulnerability Management
Analyst-led triage against live exploits, not CVSS scores. Unpatched CVEs trigger SIEM detection.

Security Awareness
Phishing simulations built from TTPs active against your sector. Training fires at the point of failure, not just once a year.
What comes next
No big-bang commitments here
only proven steps.

Discover
We learn your environment, current coverage, and what's keeping you up at night. No pitch, we need to understand before we recommend.
See it live
A working demo with real dashboards and real escalations. You'll see what it actually looks like to be a OneAxiom customer.
Go live
Custom detections deployed. Consistent team operating. Full SOC coverage active. Hands-on from day one.
Compliance-driven security
Your auditors don't care that your team is small.
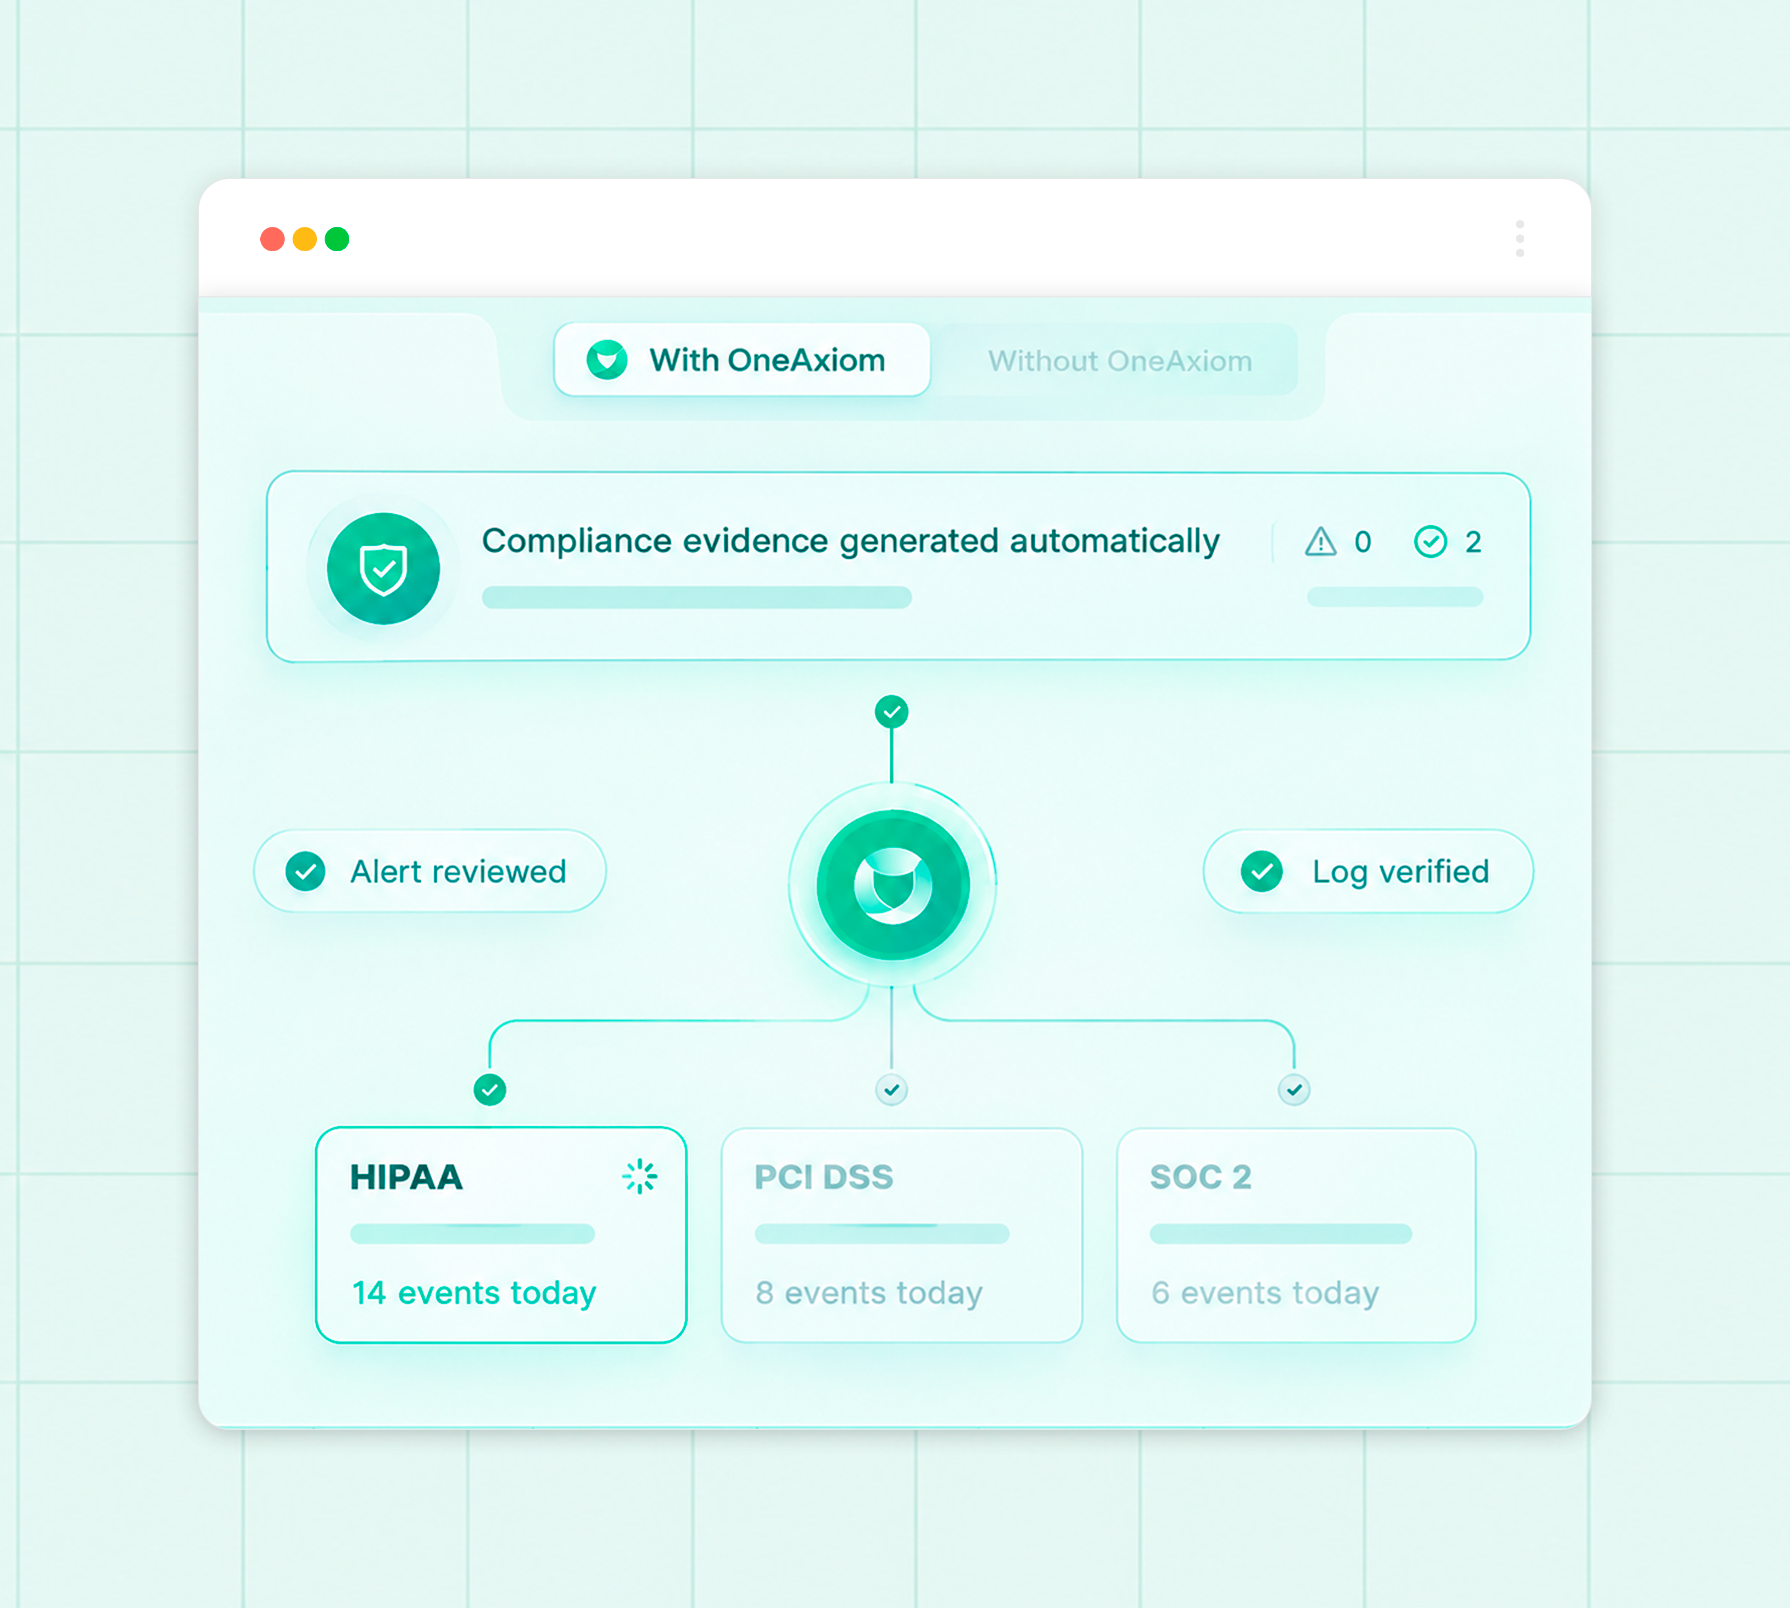
The evidence requirements are the same as a Fortune 500's. OneAxiom produces audit evidence continuously for HIPAA, PCI DSS, SOC 2, NIST, and more, as a byproduct of operational work. No scramble the week before your QSA shows up.
How is OneAxiom priced?
Flat-rate, predictable pricing.
You can see the model on our pricing page before you ever talk to sales.
How long does onboarding take?
Most customers are fully onboarded within a few weeks, depending on environment complexity.
Do you replace our internal IT or security team?
No, we work alongside your team as a consistent extension of it, not a replacement.
What tools do we need to buy first?
None. OneAxiom is built to work with your existing stack wherever possible.
What happens during an incident?
Your accountable team leads response immediately, with IR included in your plan.
Got questions
Frequently asked
and answered
Book a 30 min call
No commitment yet. We'll walk through your environment and see if there's a fit.