
Security Observability Assessment
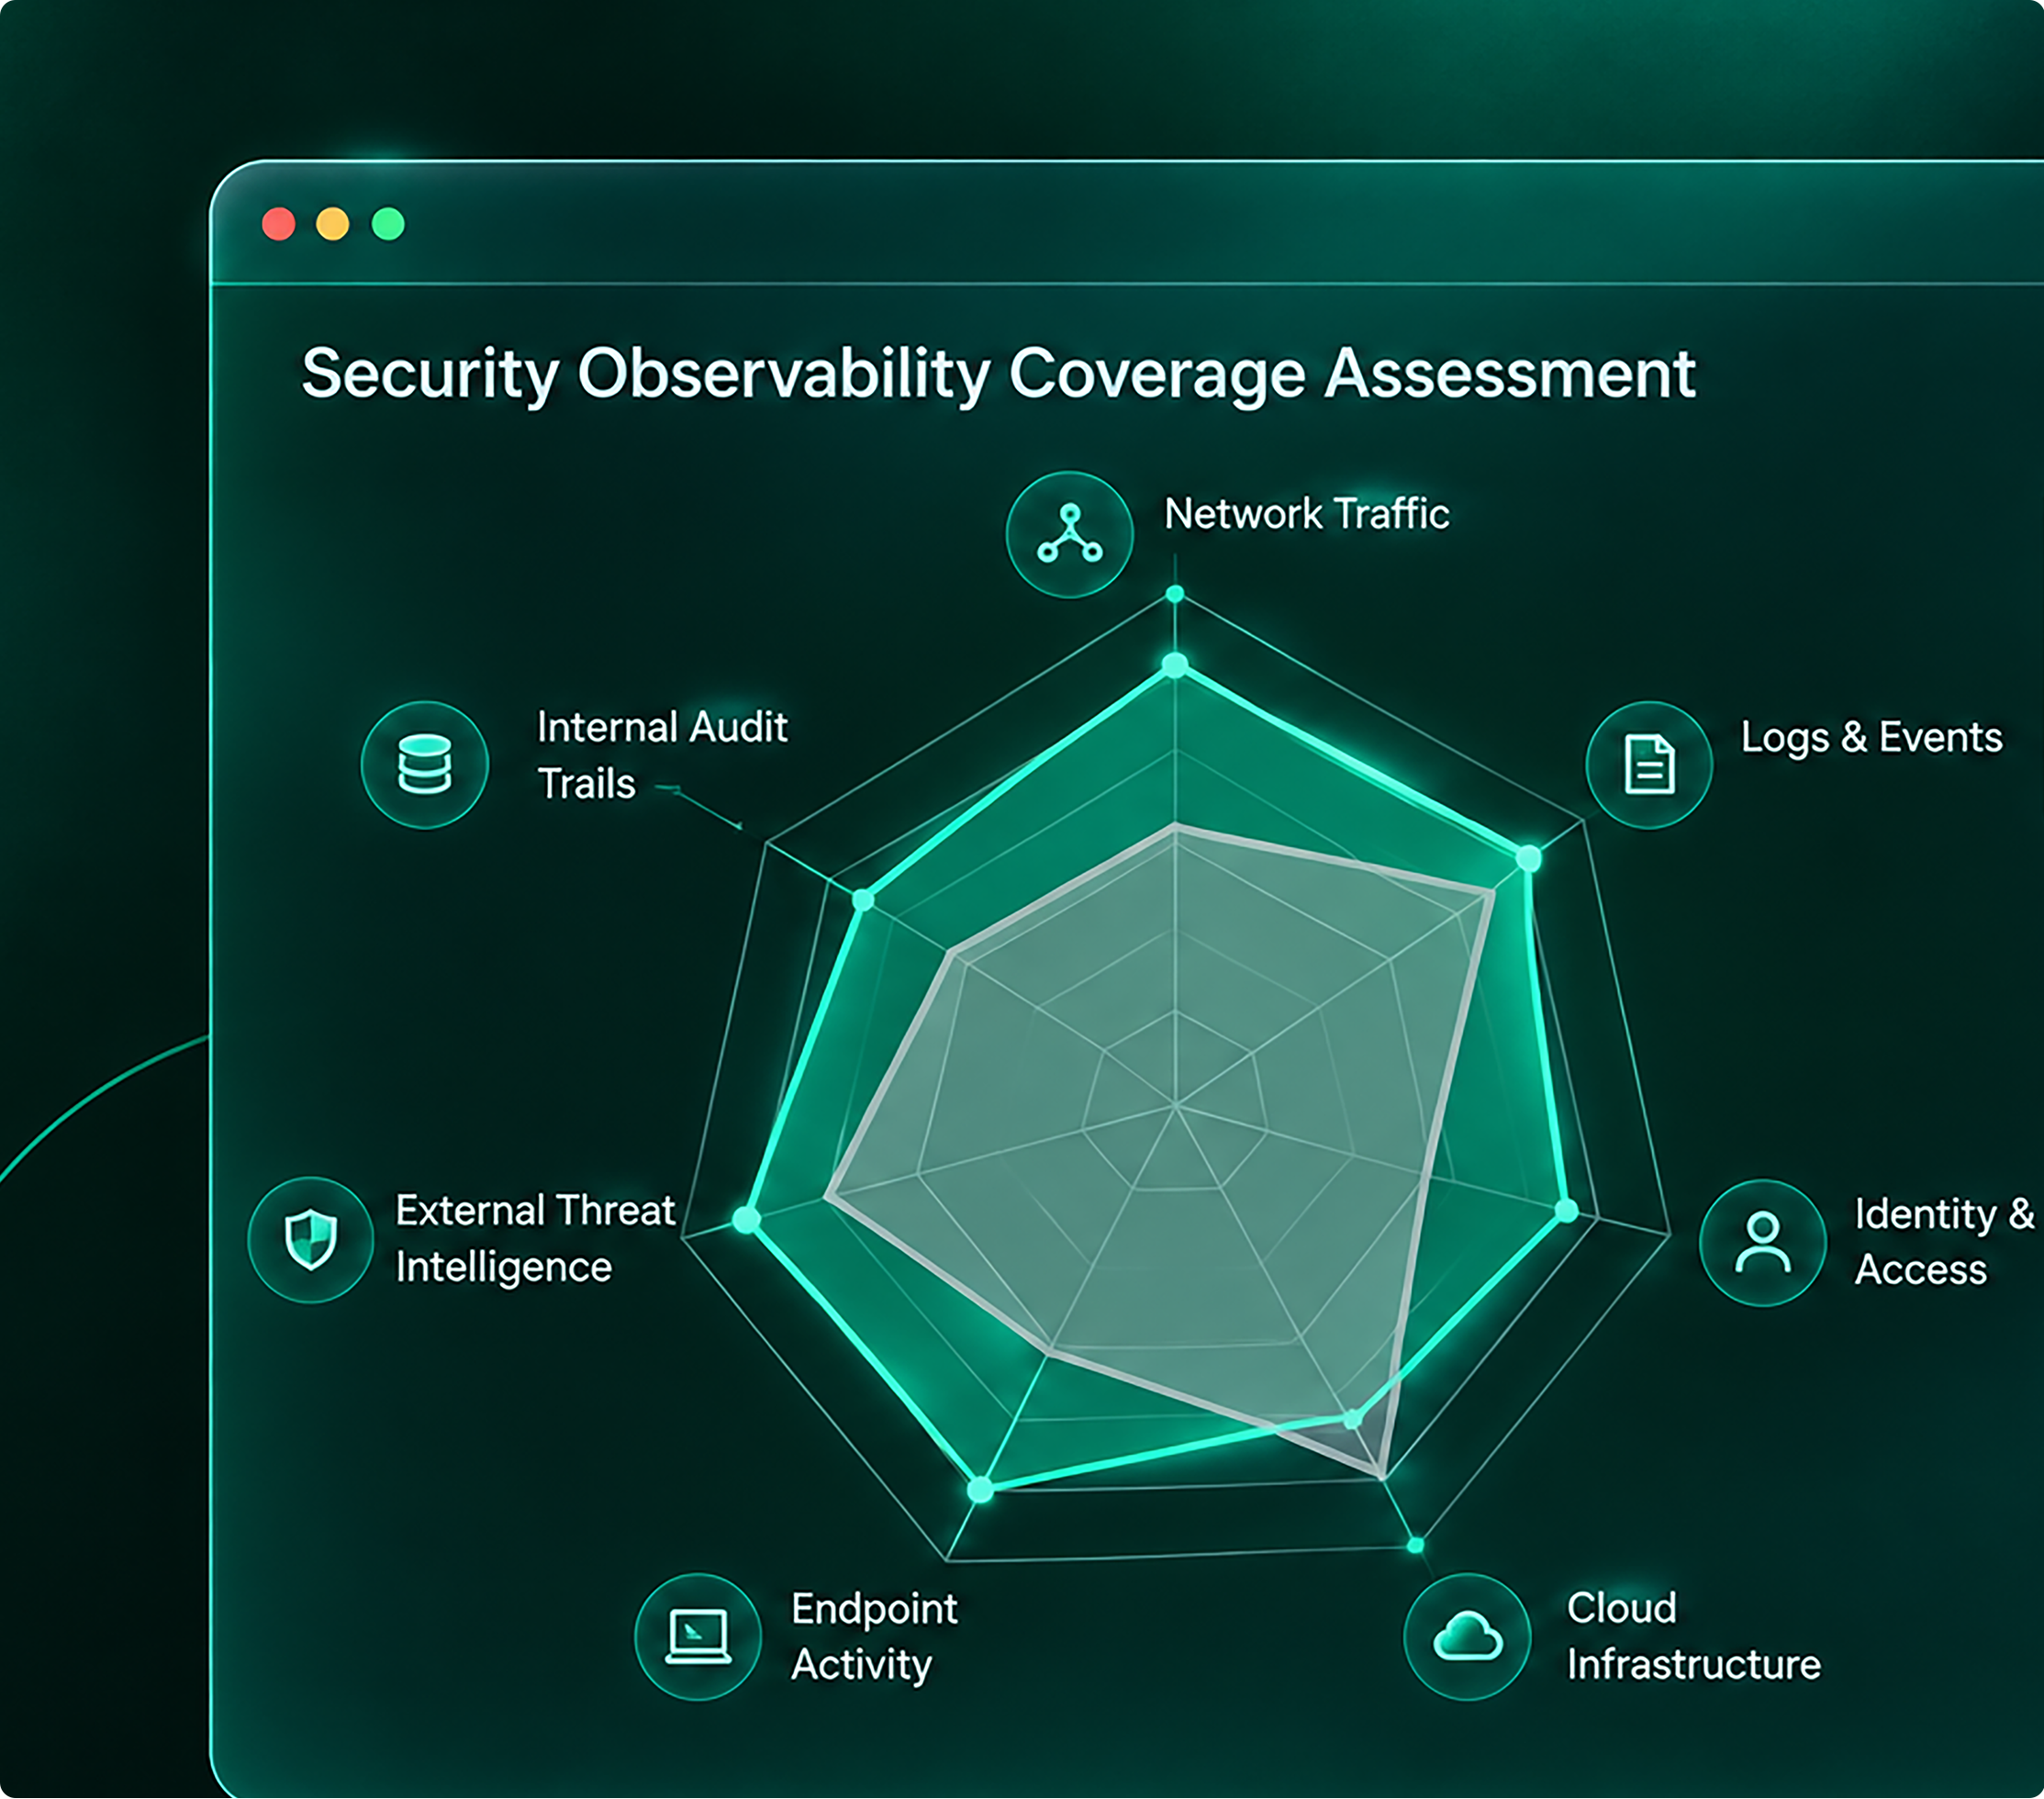
Find out exactly what your
environment can and can't see.
no waiting
independently
the assessment
How it works
Three simple steps.Your results are just one form away

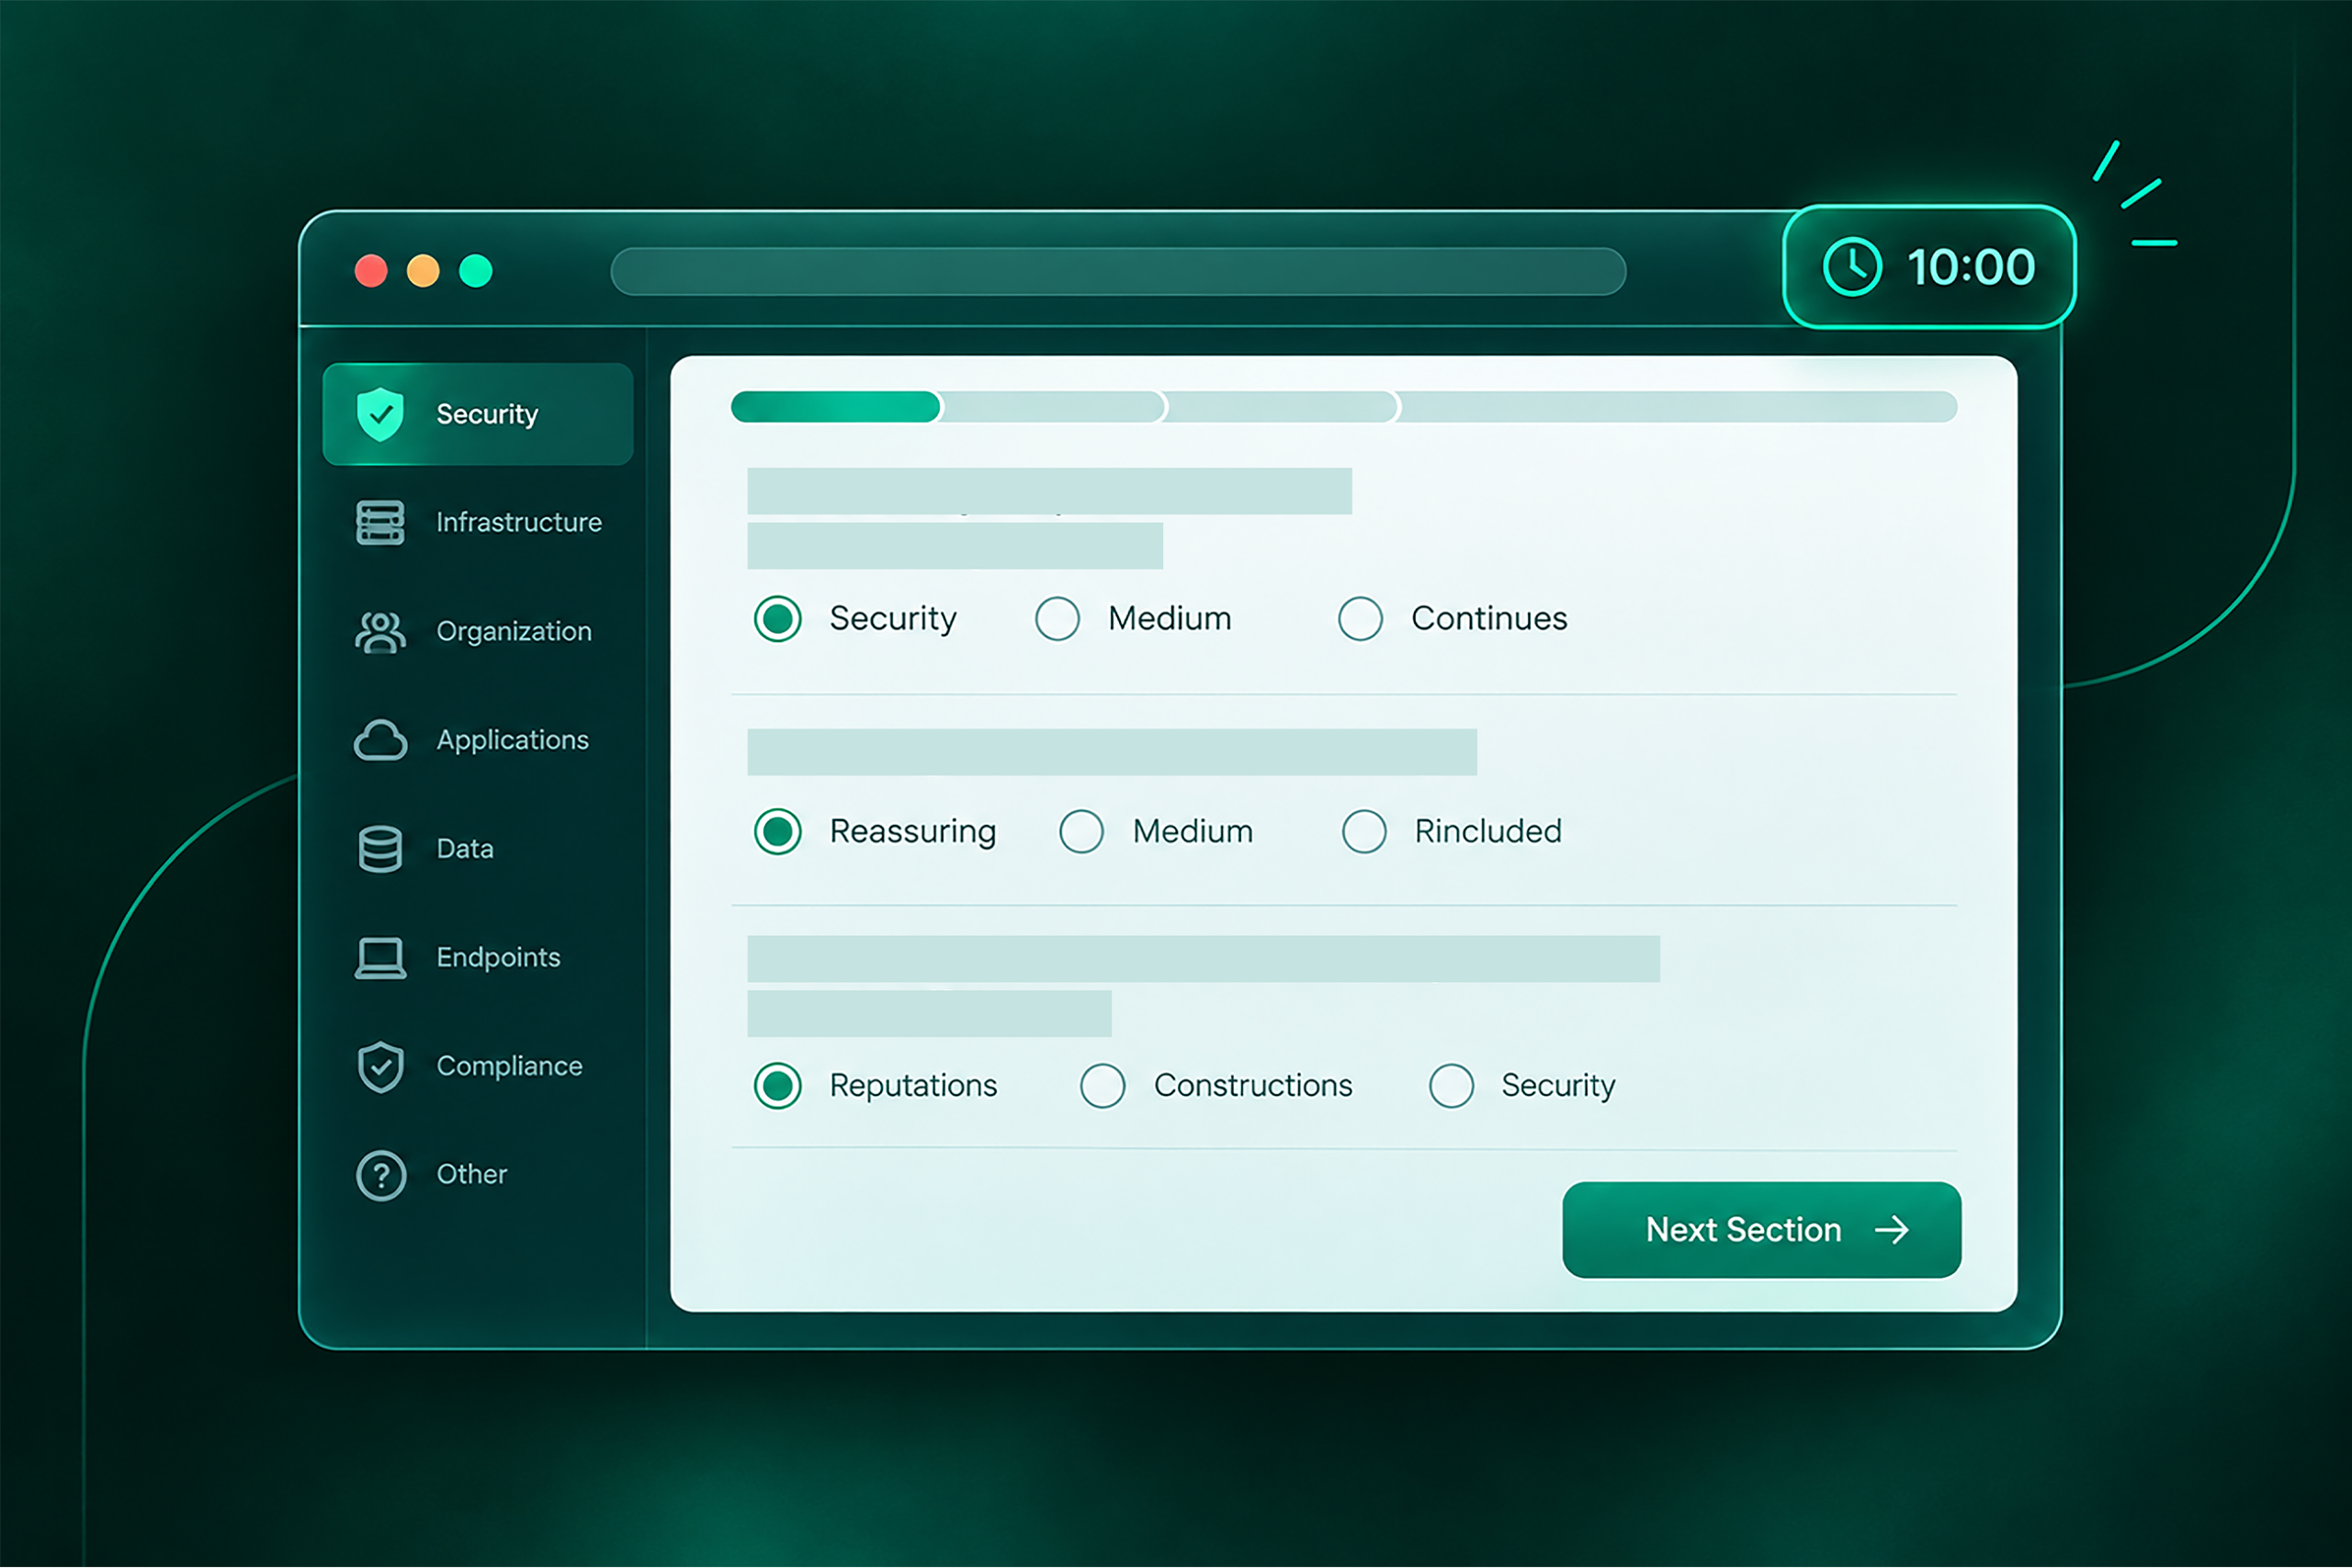
Answer the questions
About 30 questions across seven domains, one domain per step, roughly 10 minutes total.
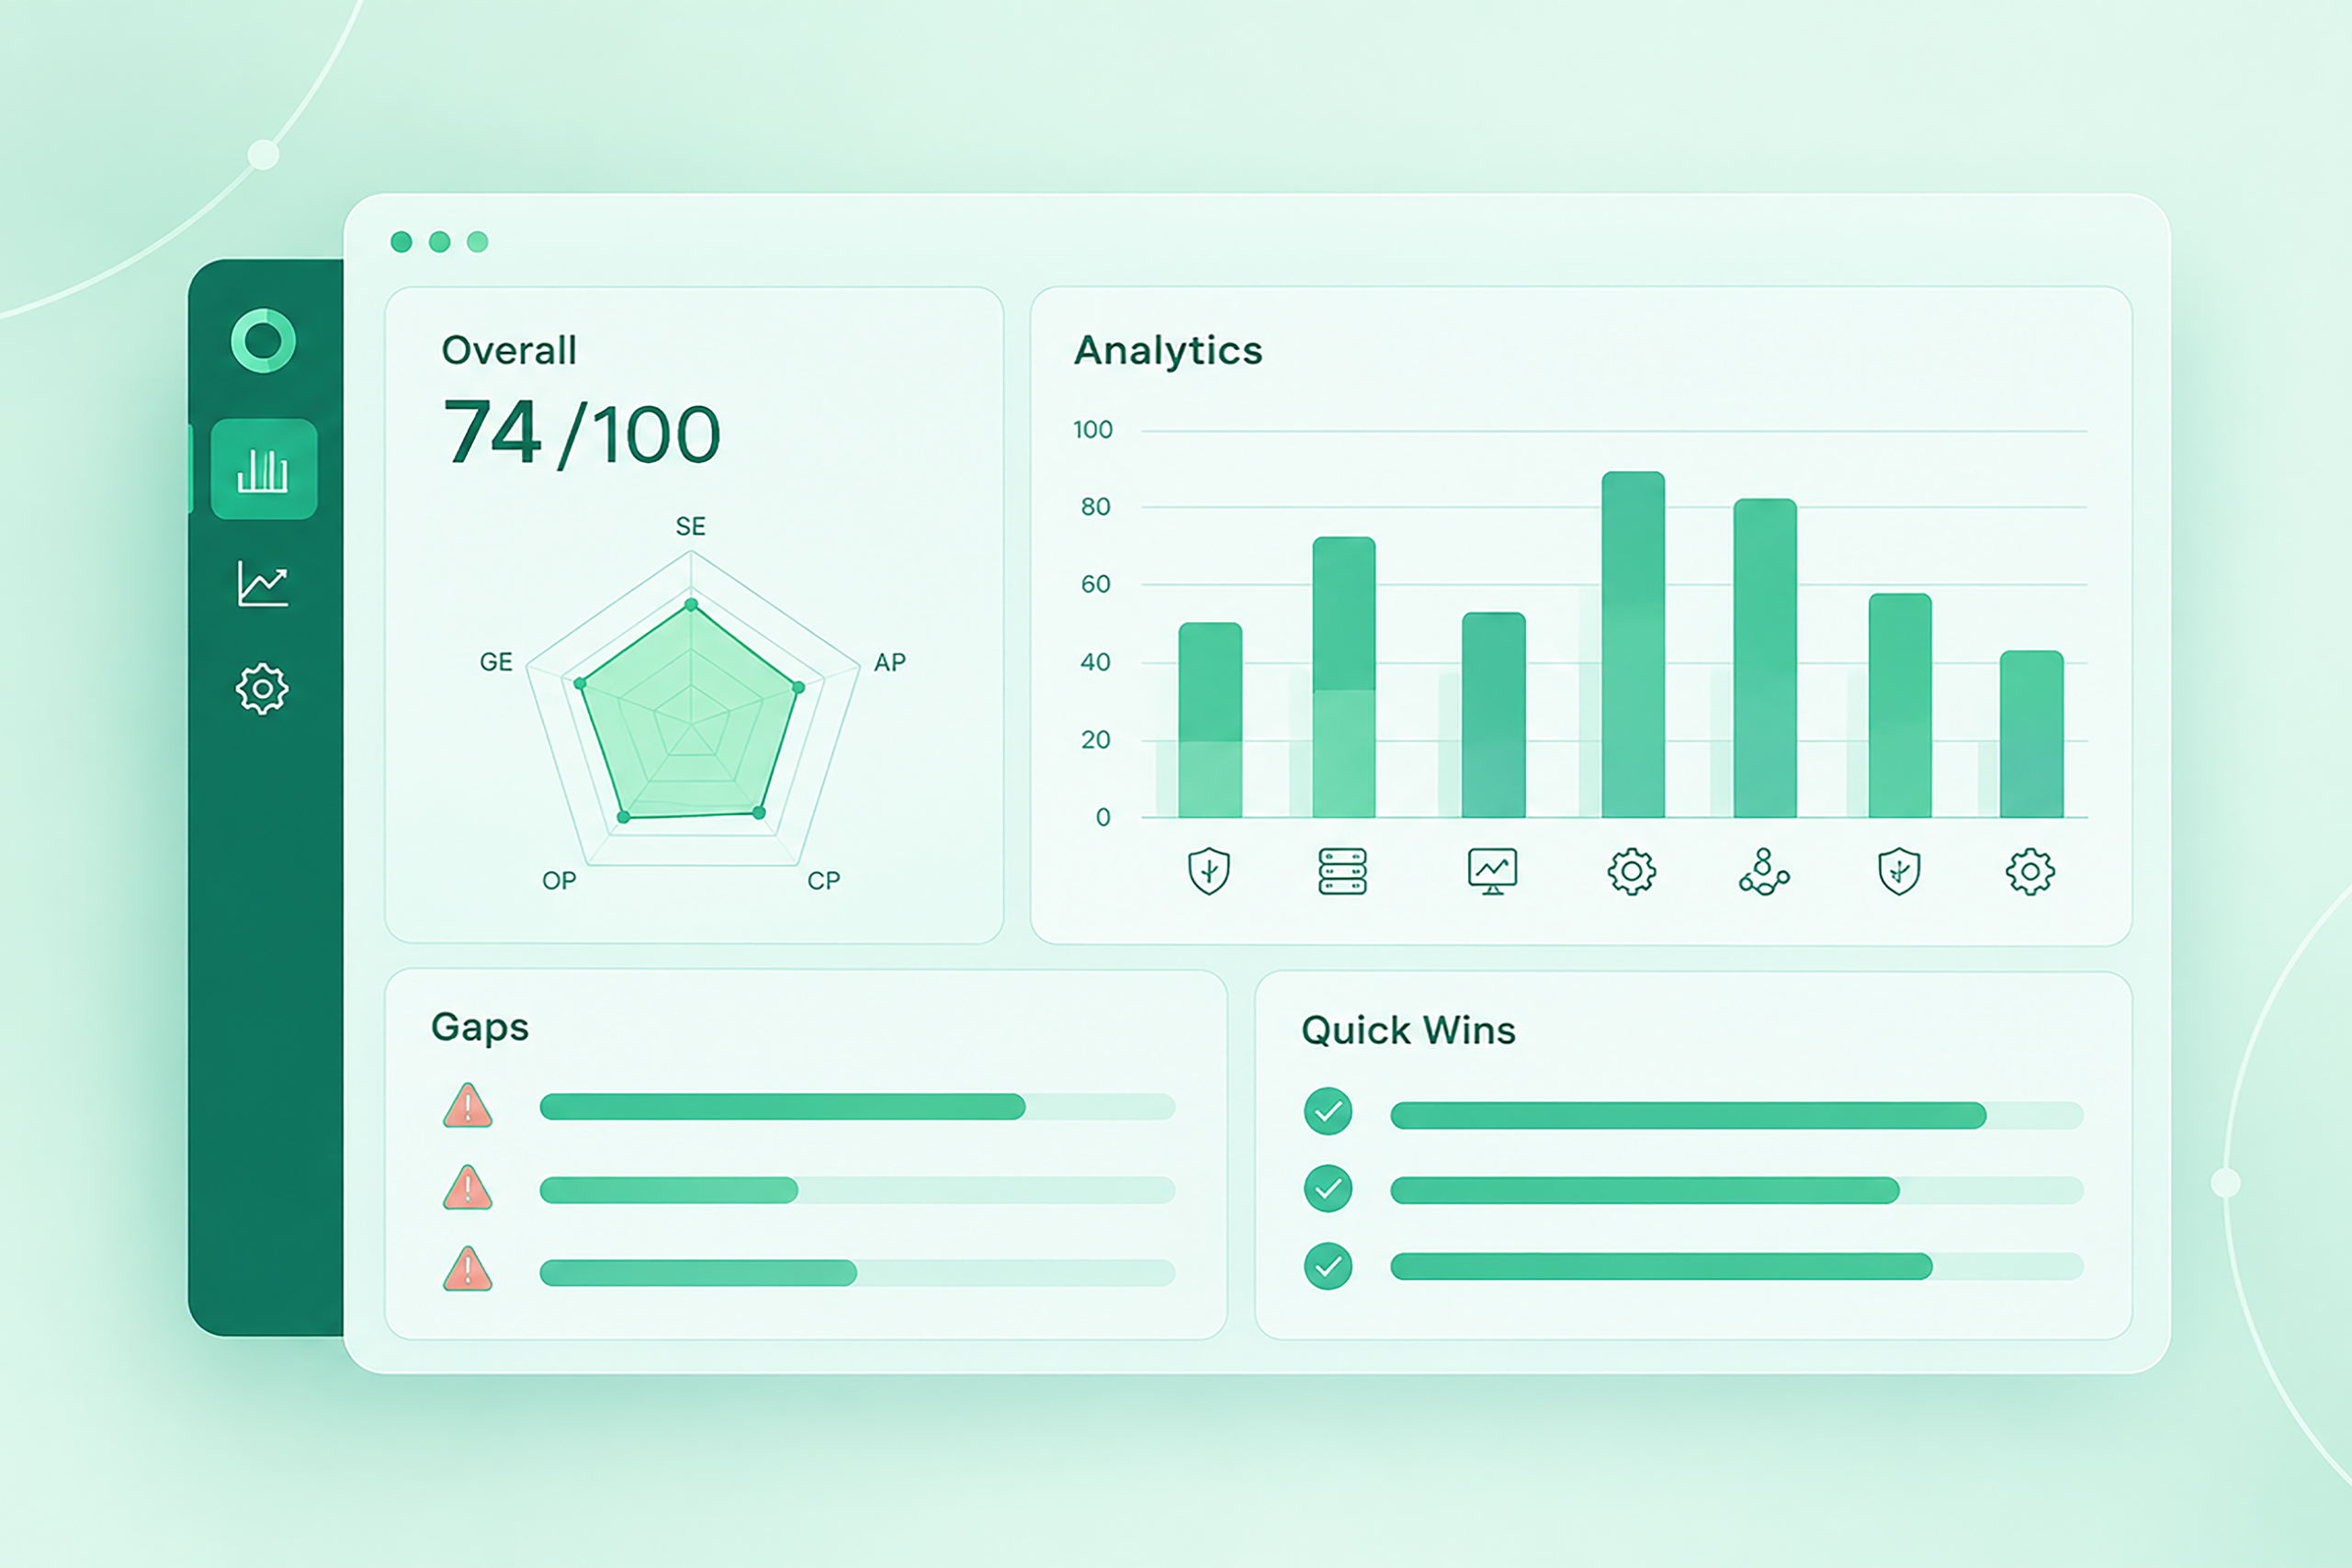
See your scored results
Your overall score, a domain breakdown, and the gaps and quick wins, the moment you finish.
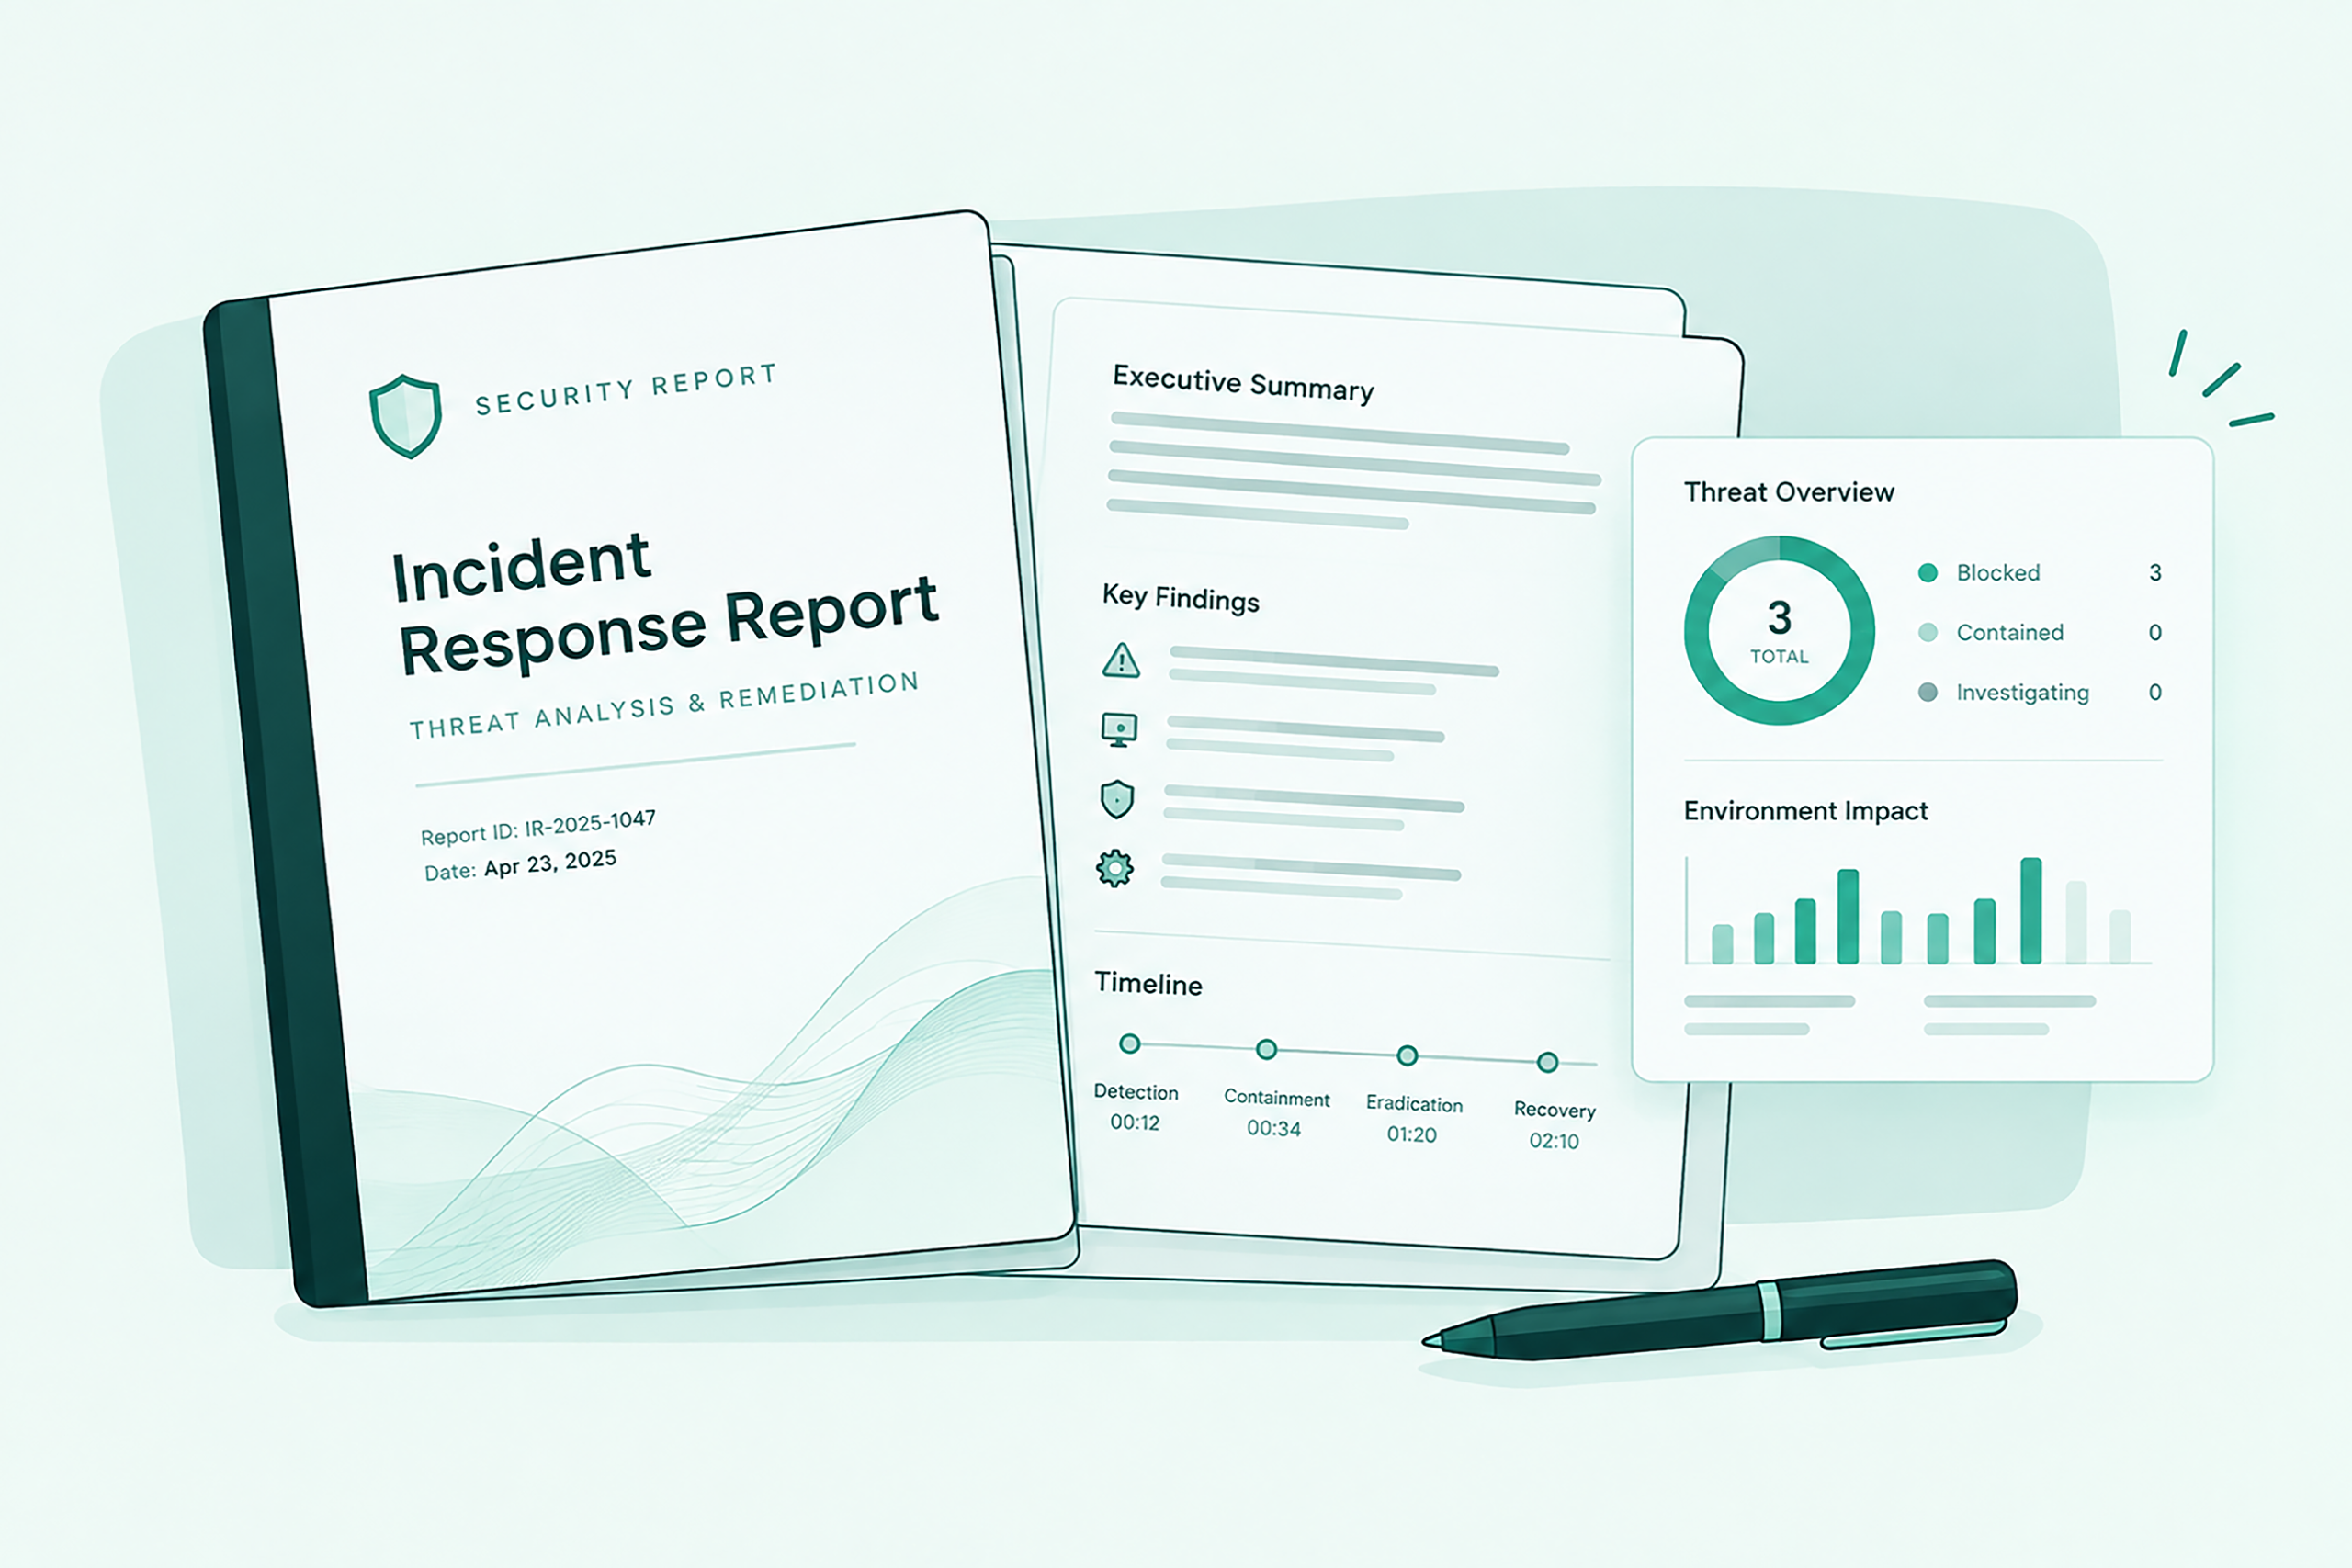
Unlock the full report
Service recommendations and a prioritized action plan, after a 30-minute call with a OneAxiom analyst.
What we deliver
Every layer managed, by
analysts who know your
environment.

The evidence requirements
Seven domains scored against real detection standards, not marketing checkboxes.

Your answers stay private
Nothing is shared or sold. Your results are yours until you choose to talk to us.

Built from real engagements
Scoring criteria drawn from actual MSSP assessments, not a generic template.


A scored picture of your security visibility. No vendor pitch attached.
Domain score breakdown
Your visibility score across cloud, identity, endpoint, network, detection, awareness, and vulnerability management, each scored independently.
Identified coverage gaps
Critical and moderate gaps flagged by domain, with context on what each gap means operationally.
Quick wins
The highest-leverage actions your team can take now, ranked by impact and effort.
Your score is the starting point. A 30-minute call turns it into service recommendations and a prioritized action plan.
After your scoreWhat the assessment covers
Identity
Authentication event logging, privilege monitoring, and detection coverage for credential-based attacks.


50+ IT teams
Have taken the scorecard
The difference
31% of breaches start with a vulnerability nobody was watching (Verizon 2026 DBIR). This scorecard tells you if yours is one of them, and shows exactly how you score across all seven domains.
Start the AssessmentHow often are phishing simulations run?
Continuously, with at minimum one formal exercise per quarter. Simulation frequency and difficulty are tuned based on your team's performance over time. If you want simulations more often than the standard monthly cadence, we'll train your team to self-manage those additional off-cadence campaigns directly in the platform.
What platform do you use?
We deliver this service through KnowBe4. OneAxiom manages the platform on your behalf: setup, campaigns, user management, reporting, and support, so you get the full capability of the platform without the overhead of running it.
Can you integrate with our HR system or Active Directory for user management?
Yes. We support Active Directory, SCIM, and Google Workspace for automated user sync, along with manual list management through your TAM for customers without automated provisioning.
What tools do we need to buy first?
None. OneAxiom is built to work with your existing stack wherever possible.
What happens when someone clicks on a phishing simulation?
A training module fires immediately in the browser, not in the next scheduled campaign. The module explains what made the simulation convincing and what to watch for. The moment of failure is the most effective time to teach.
How do you handle users who repeatedly fail phishing simulations?
Repeat offenders are tracked and surfaced in the monthly report. We flag them to your designated contact. What happens next, whether that's additional training, manager notification, or HR involvement, is your organization's call. We provide the data. Disciplinary decisions are yours.
Do you produce reports for compliance or cyber insurance purposes?
We don't produce a single standard report, since different frameworks and different auditors tend to ask for different things. What we do is help gather or generate the specific artifacts your auditor or insurer requires, built to their request rather than off a template.
What if our team has low participation rates?
Participation depends partly on internal leadership sponsorship: we flag the issue, you have the lever to pull. On the platform side, we adjust reminder cadence, escalate delinquencies to your contact, and can recommend training content that tends to drive higher engagement. Any users not completing mandatory training get raised with your team during your regular review meetings or by email, depending on how often those meetings happen.
Got questions
Frequently asked
Observability Scorecard
Book a 30 min call
No pitch, no pressure. We'll walk through your environment and see if there's a fit.