Managed EDR / MDR
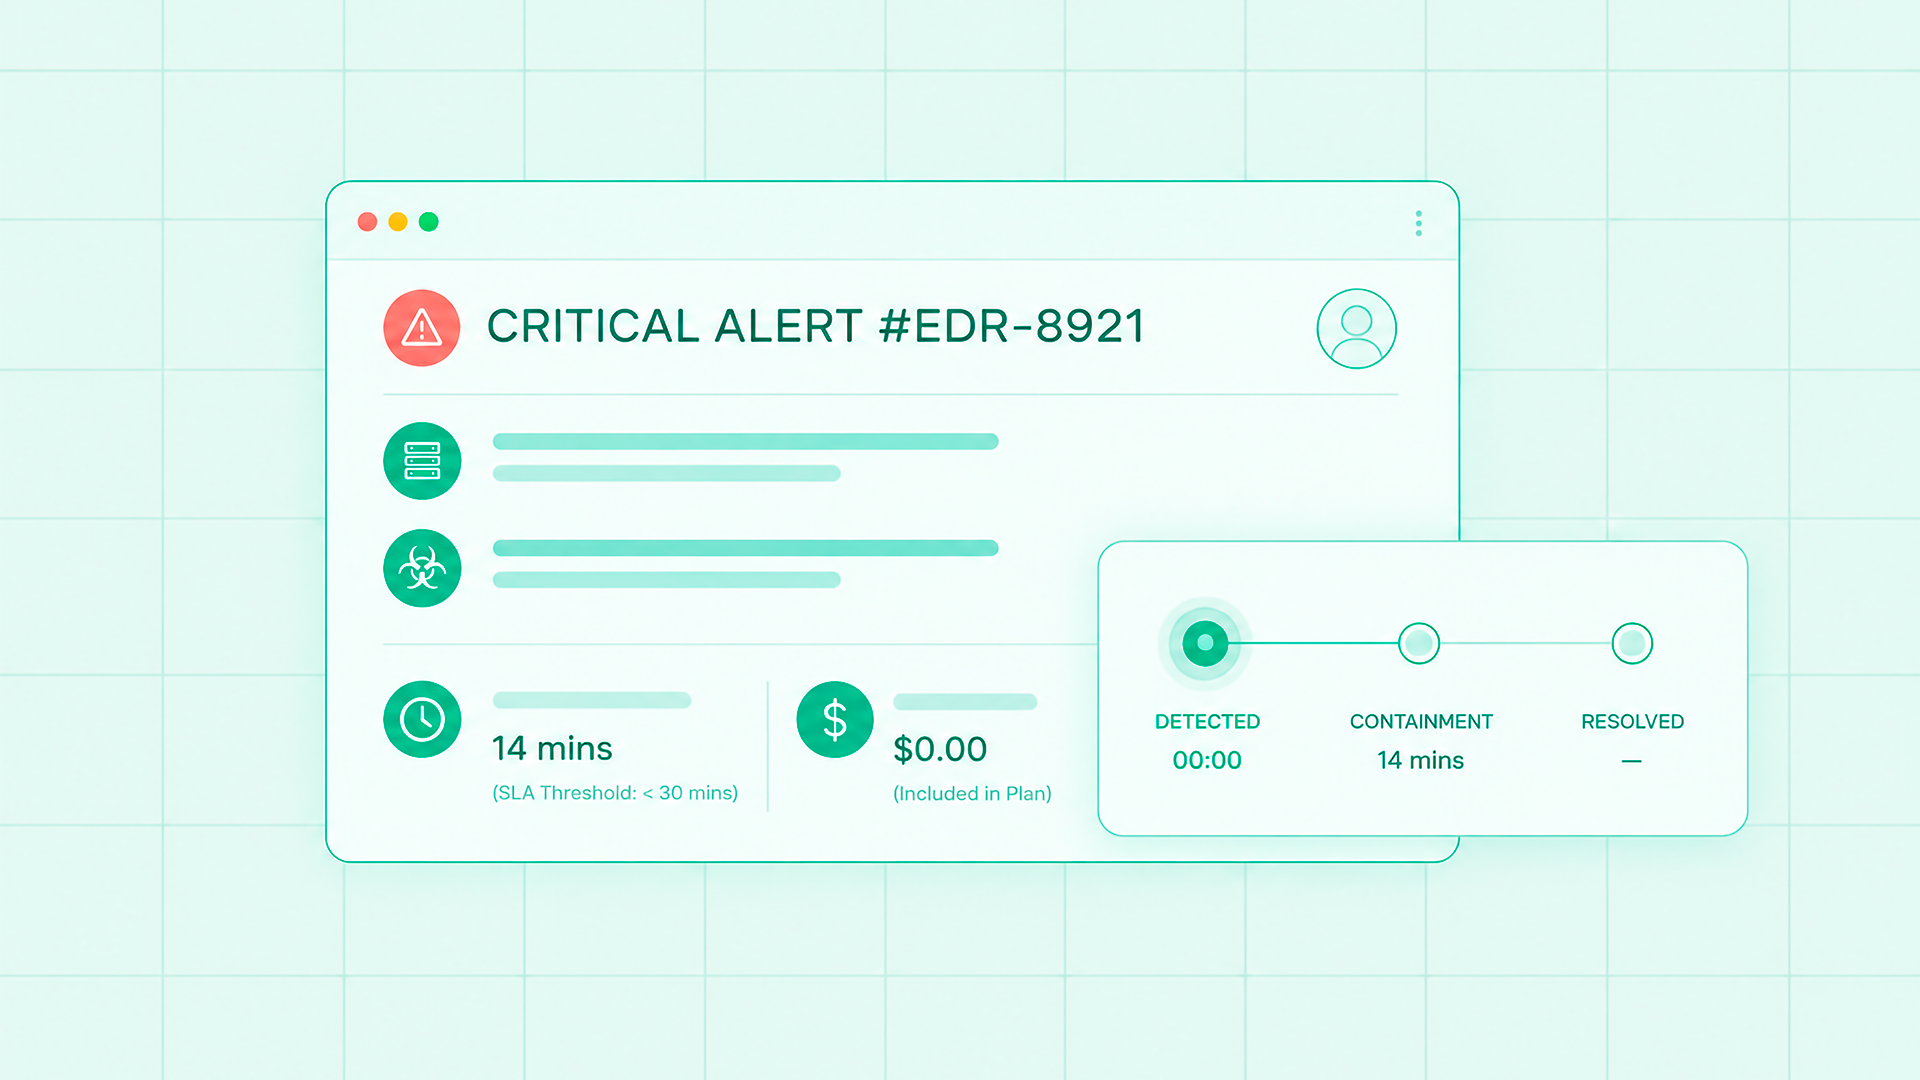
Endpoints monitored.
Threats contained in 30 minutes.
Most EDR tools sit deployed and unwatched. Ours are monitored 24/7 by the analysts who tune your detection rules. When something fires, they respond, no handoff, no ramp-up. Built-in IR, no retainer.
phone escalations
across our customer base
(no retainer needed)
for all tiers (T1-T3)
Escalation Tiers
When a threat is confirmed, the team
already knows your environment.
Catch & Filter
AI pre-screens endpoint telemetry. T1 analyst catches behavioral anomalies.

Validate & Contextualize
T2 analyst validates the threat against your environment's baseline and whitelists.
Immediate Containment
T3 analyst isolates the endpoint, kills the process, and preserves artifacts.
How it works
Deployed, monitored, and ready to
respond from day one.

Baseline & deployment
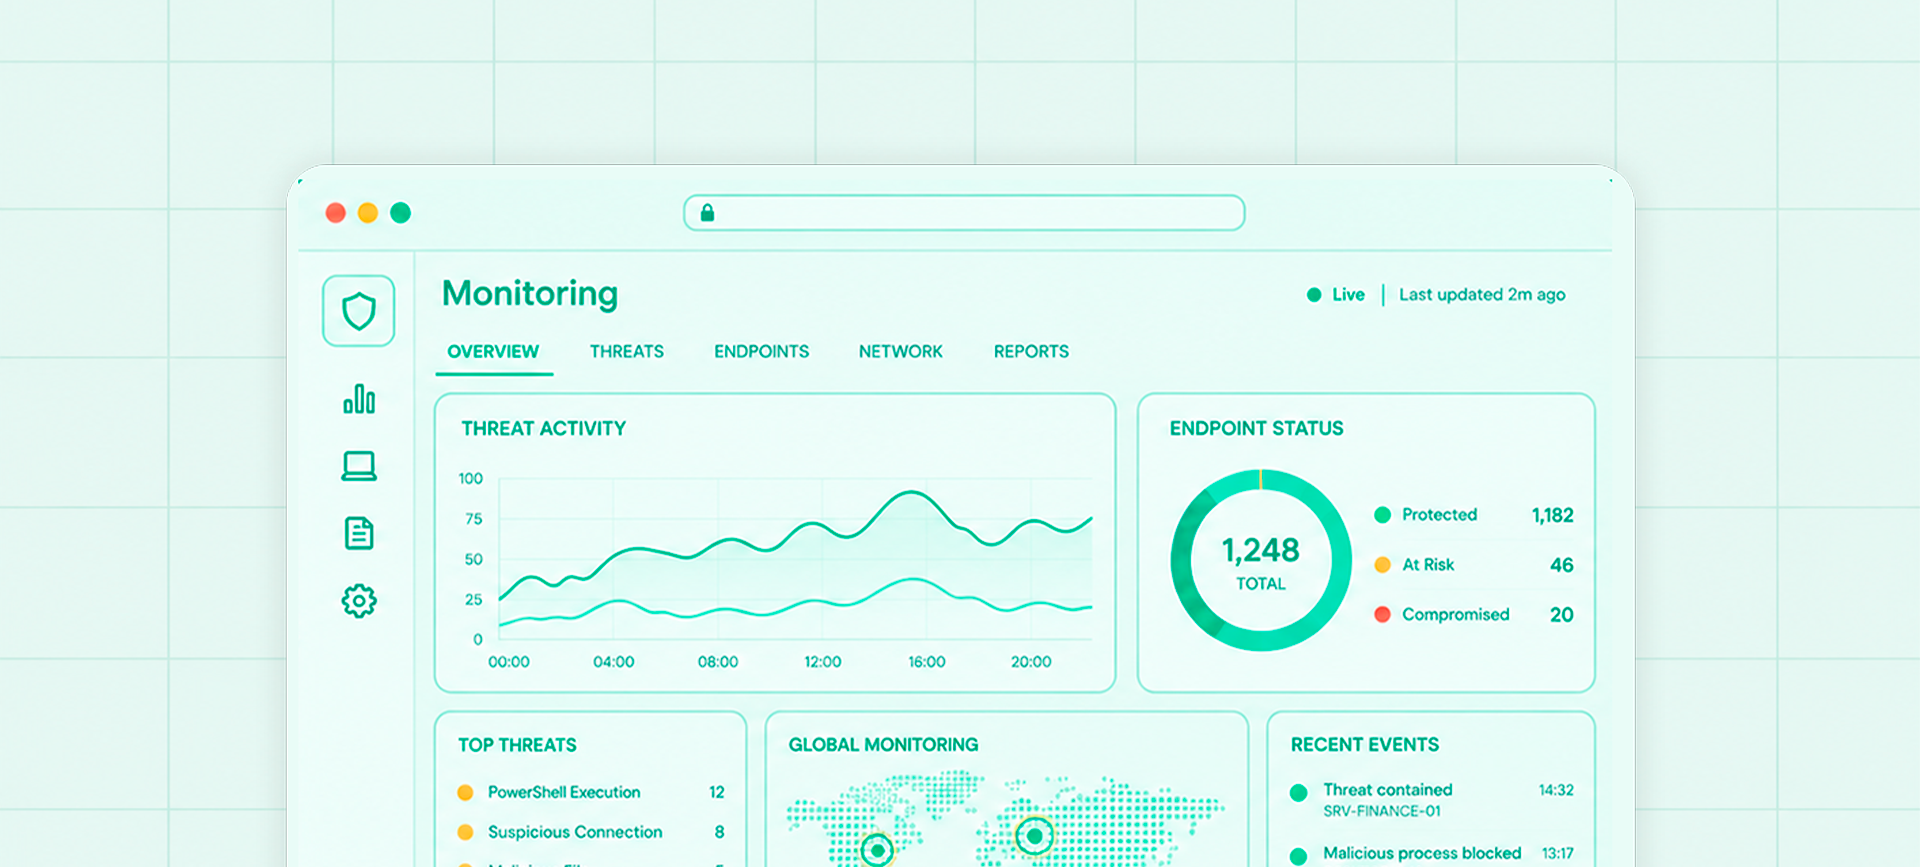
Analyst reviews inventory, OS, and app behavior, then delivers a config plan. Your team deploys agents with our support; syncs confirm coverage.

Behavioral detection tuning
Known-good behavior is whitelisted, specific assets, files, and programs, so alerts stay accurate from day one.

24/7 triage & containment
Every alert is reviewed by the analyst on shift. Confirmed threats trigger immediate containment and isolation.

Documentation & tuning
Every incident gets a written summary of detection, actions, and scope. Whitelists adjust as your infrastructure changes.
Human-in-the-loop AI
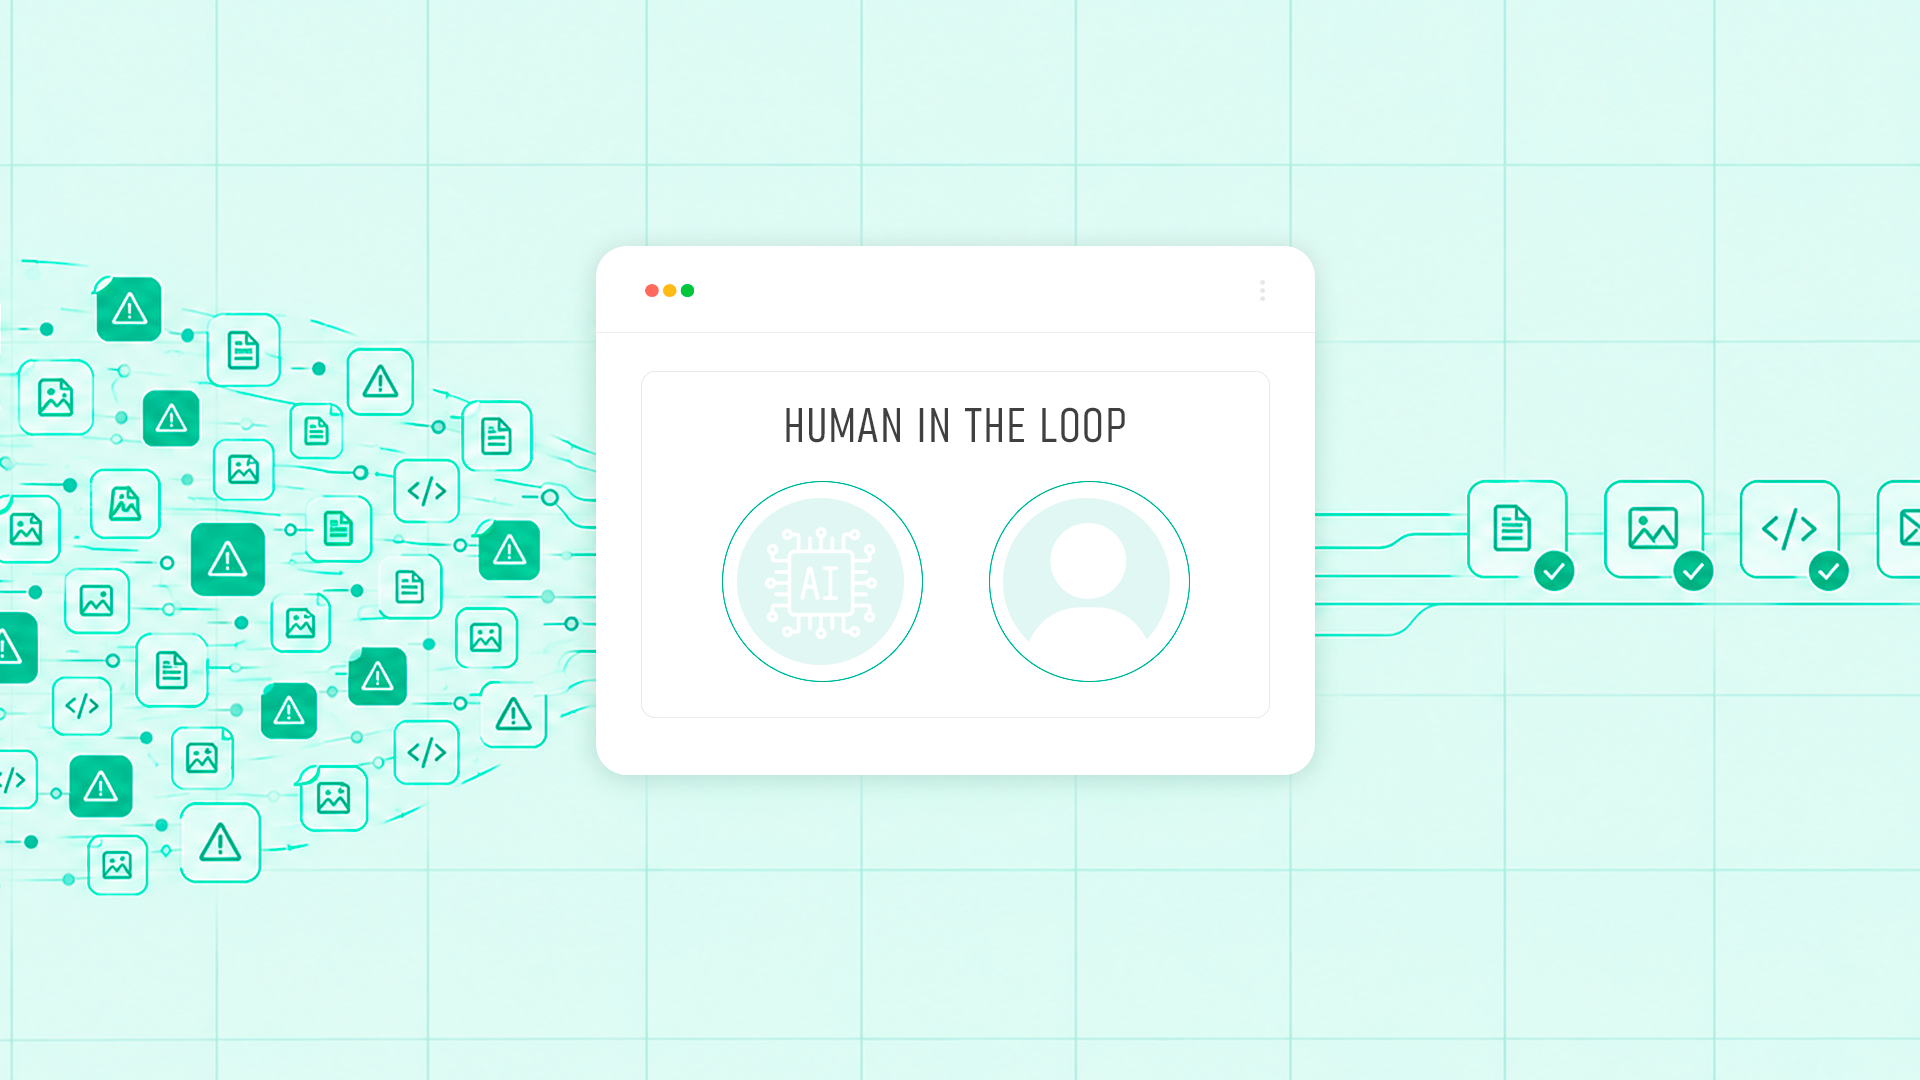
AI handles the volume.
Analysts handle the judgment.
Pre-screening endpoint telemetry and surfacing behavioral anomalies, eliminating obvious noise.
Decide whether a confirmed anomaly is an actual threat, make containment calls, or talk to your team.
The present (and future) of SecOps
Cookie-cutter security doesn't cut it anymore.
What's at stake
Threat Response
Incident Response Costs
Endpoint Coverage
Alert Noise
Unwatched EDR tool

OneAxiom managed EDR

How we stay accountable
You always know who is watching and what they are seeing.

CX Manager
Owns the executive relationship, service health, and On-Demand Executive Business Reviews.

Technical Account Manager
Owns the detection program, monthly operational reviews, and security maturity tracking.

SOC Analyst(s)
Work your environment 24/7, tune detection, triage alerts, and lead threat containment.

Threat Hunter
Builds and updates proactive detection against emerging endpoint TTPs, shared across our full customer base.
How is OneAxiom priced?
Flat-rate, predictable pricing. No log-volume surprises and no separate IR retainer for the first 10 hours each month. You can see the model on our pricing page before you ever talk to sales.
How long does onboarding take?
Most customers are fully onboarded within a few weeks, depending on environment complexity.
Do you replace our internal IT or security team?
No, we work alongside your team as a consistent extension of it, not a replacement.
What tools do we need to buy first?
None. OneAxiom is built to work with your existing stack wherever possible.
What happens during an incident?
Your accountable team leads response immediately, with IR included in your plan.
Do I need to replace my current EDR platform?
We support CrowdStrike and SentinelOne. If your platform is something else, you'd migrate to one of these, managed by us.
Who deploys the EDR agents?
Your IT team does. We provide documentation, support, and run frequent syncs to confirm coverage.
Got questions
Frequently asked
Managed EDR/MDR
Book a 30 min call
No commitment yet. We'll walk through your environment and see if there's a fit.