Security Awareness Training
Checkbox training doesn't change behavior. Point-of-failure training does.
Outdated annual training won't stop phishing. We run a continuous program: threat-aligned simulations, instant training upon failure, and metrics tracking real behavior, not completion rates.
in your SOW
and industry
user data speed
How it works
Training is the easy part. Follow-through is what makes it work.
One-time setup. Tenant configured, users synced, first campaign validated before launch.
1. Tenant & Branding Setup
KnowBe4 tenant configured with your branding, domains, and admin access controls.
2. Identity Provider Integration
Automated sync via Active Directory, SCIM, or Google Workspace (or manual list via TAM with 4-hr SLA for changes).
3. Threat-Aligned Template Build
Senior SOC Analysts build custom phishing templates tailored to your specific industry and vertical risks.
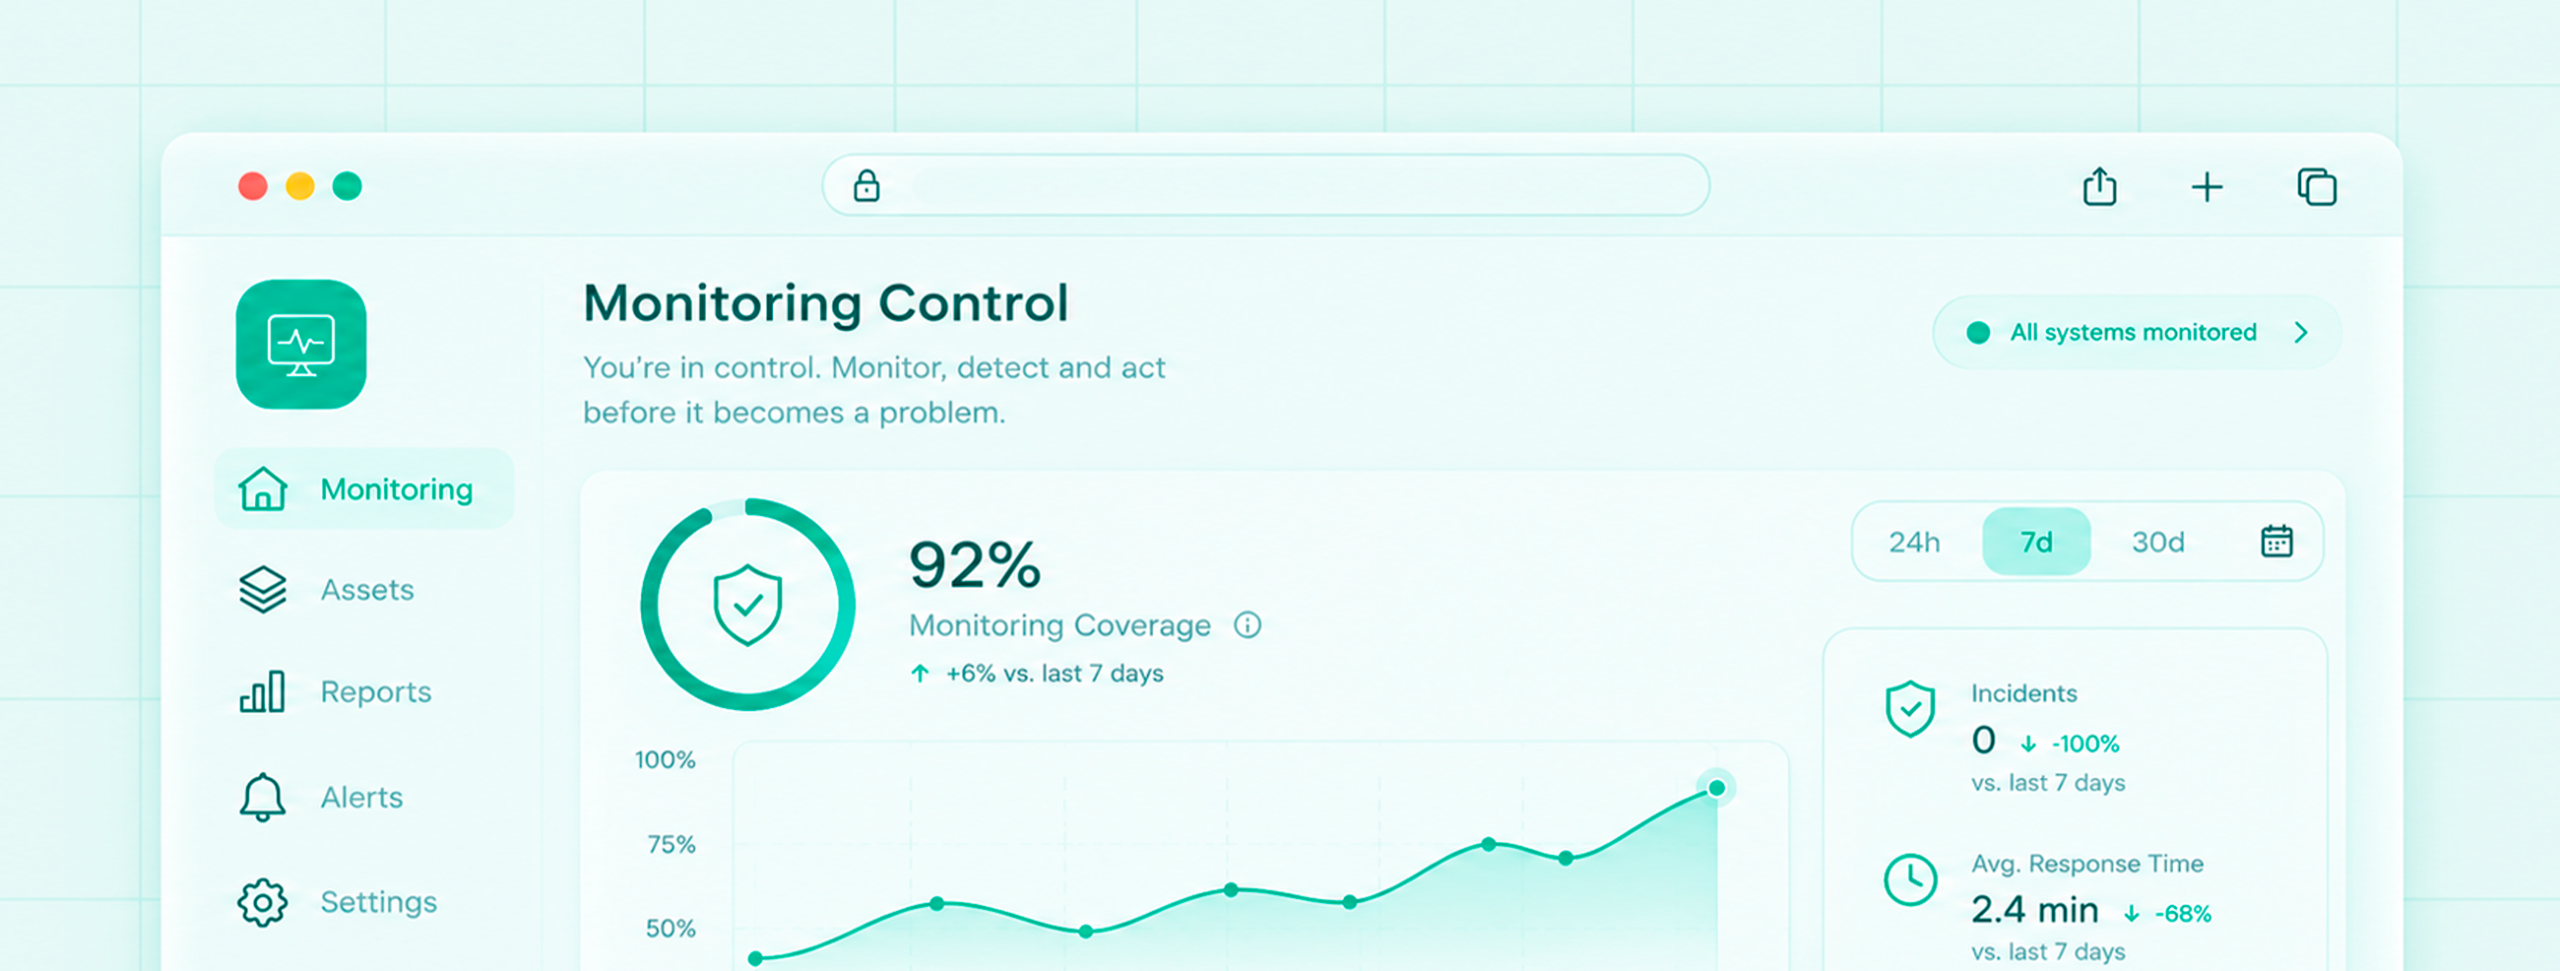
Ongoing operation. Campaigns launch on cadence, results tracked, and every click becomes a teaching moment.
1. Threat-Tuned Campaign Launch
Simulations run monthly in practice, at minimum quarterly per your SOW, using templates built for threats active in your industry.
2. Point-of-Failure Training
A click launches a training module in the browser immediately, explaining what made the simulation convincing and what to watch for.
3. Behavior Tracking & Escalation
Click-rate trends and repeat-miss patterns are tracked by department, with repeat offenders flagged to your designated contact for follow-up.
Why this matters
Running simulations isn't a training program. Here's the difference.
Behavior changes, not just completion rates
Completion rates tell you who finished the module. Click rate trends tell you whether behavior is actually changing.
Training fires at the point of failure
When someone clicks a simulated phishing link, training launches in their browser immediately, not in the next scheduled campaign.
Risk is tracked, not assumed
Monthly reports show completion rates, click trends, and department risk scores. The program never resets.
Your SOC gets smarter too
Repeat-click patterns become part of your ongoing risk profile, reviewed alongside the rest of your security program.
How often are phishing simulations run?
Continuously, with at minimum one formal exercise per quarter. Simulation frequency and difficulty are tuned based on your team's performance over time.
If you want simulations more often than the standard monthly cadence, we'll train your team to self-manage those additional off-cadence campaigns directly in the platform.
Can you integrate with our HR system or Active Directory for user management?
Yes. We support Active Directory, SCIM, and Google Workspace for automated user sync, along with manual list management through your TAM for customers without automated provisioning.
What tools do we need to buy first?
None. OneAxiom is built to work with your existing stack wherever possible.
What happens when someone clicks on a phishing simulation?
A training module fires immediately in the browser, not in the next scheduled campaign.
The module explains what made the simulation convincing and what to watch for. The moment of failure is the most effective time to teach.
How do you handle users who repeatedly fail phishing simulations?
Repeat offenders are tracked and surfaced in the monthly report. We flag them to your designated contact.
What happens next, whether that's additional training, manager notification, or HR involvement, is your organization's call.
Do you produce reports for compliance or cyber insurance purposes?
We don't produce a single standard report, since different frameworks and different auditors tend to ask for different things.
What we do is help gather or generate the specific artifacts your auditor or insurer requires, built to their request rather than off a template.
What if our team has low participation rates?
Participation depends partly on internal leadership sponsorship: we flag the issue, you have the lever to pull.
On the platform side, we adjust reminder cadence, escalate delinquencies to your contact, and can recommend training content that tends to drive higher engagement.
Any users not completing mandatory training get raised with your team during your regular review meetings or by email, depending on how often those meetings happen.
Got questions
Frequently asked
Security Awareness Training
Book a 30 min call
No commitment yet. We'll walk through your environment and see if there's a fit.