Managed SIEM
Stop managing a tool and start running a security program.
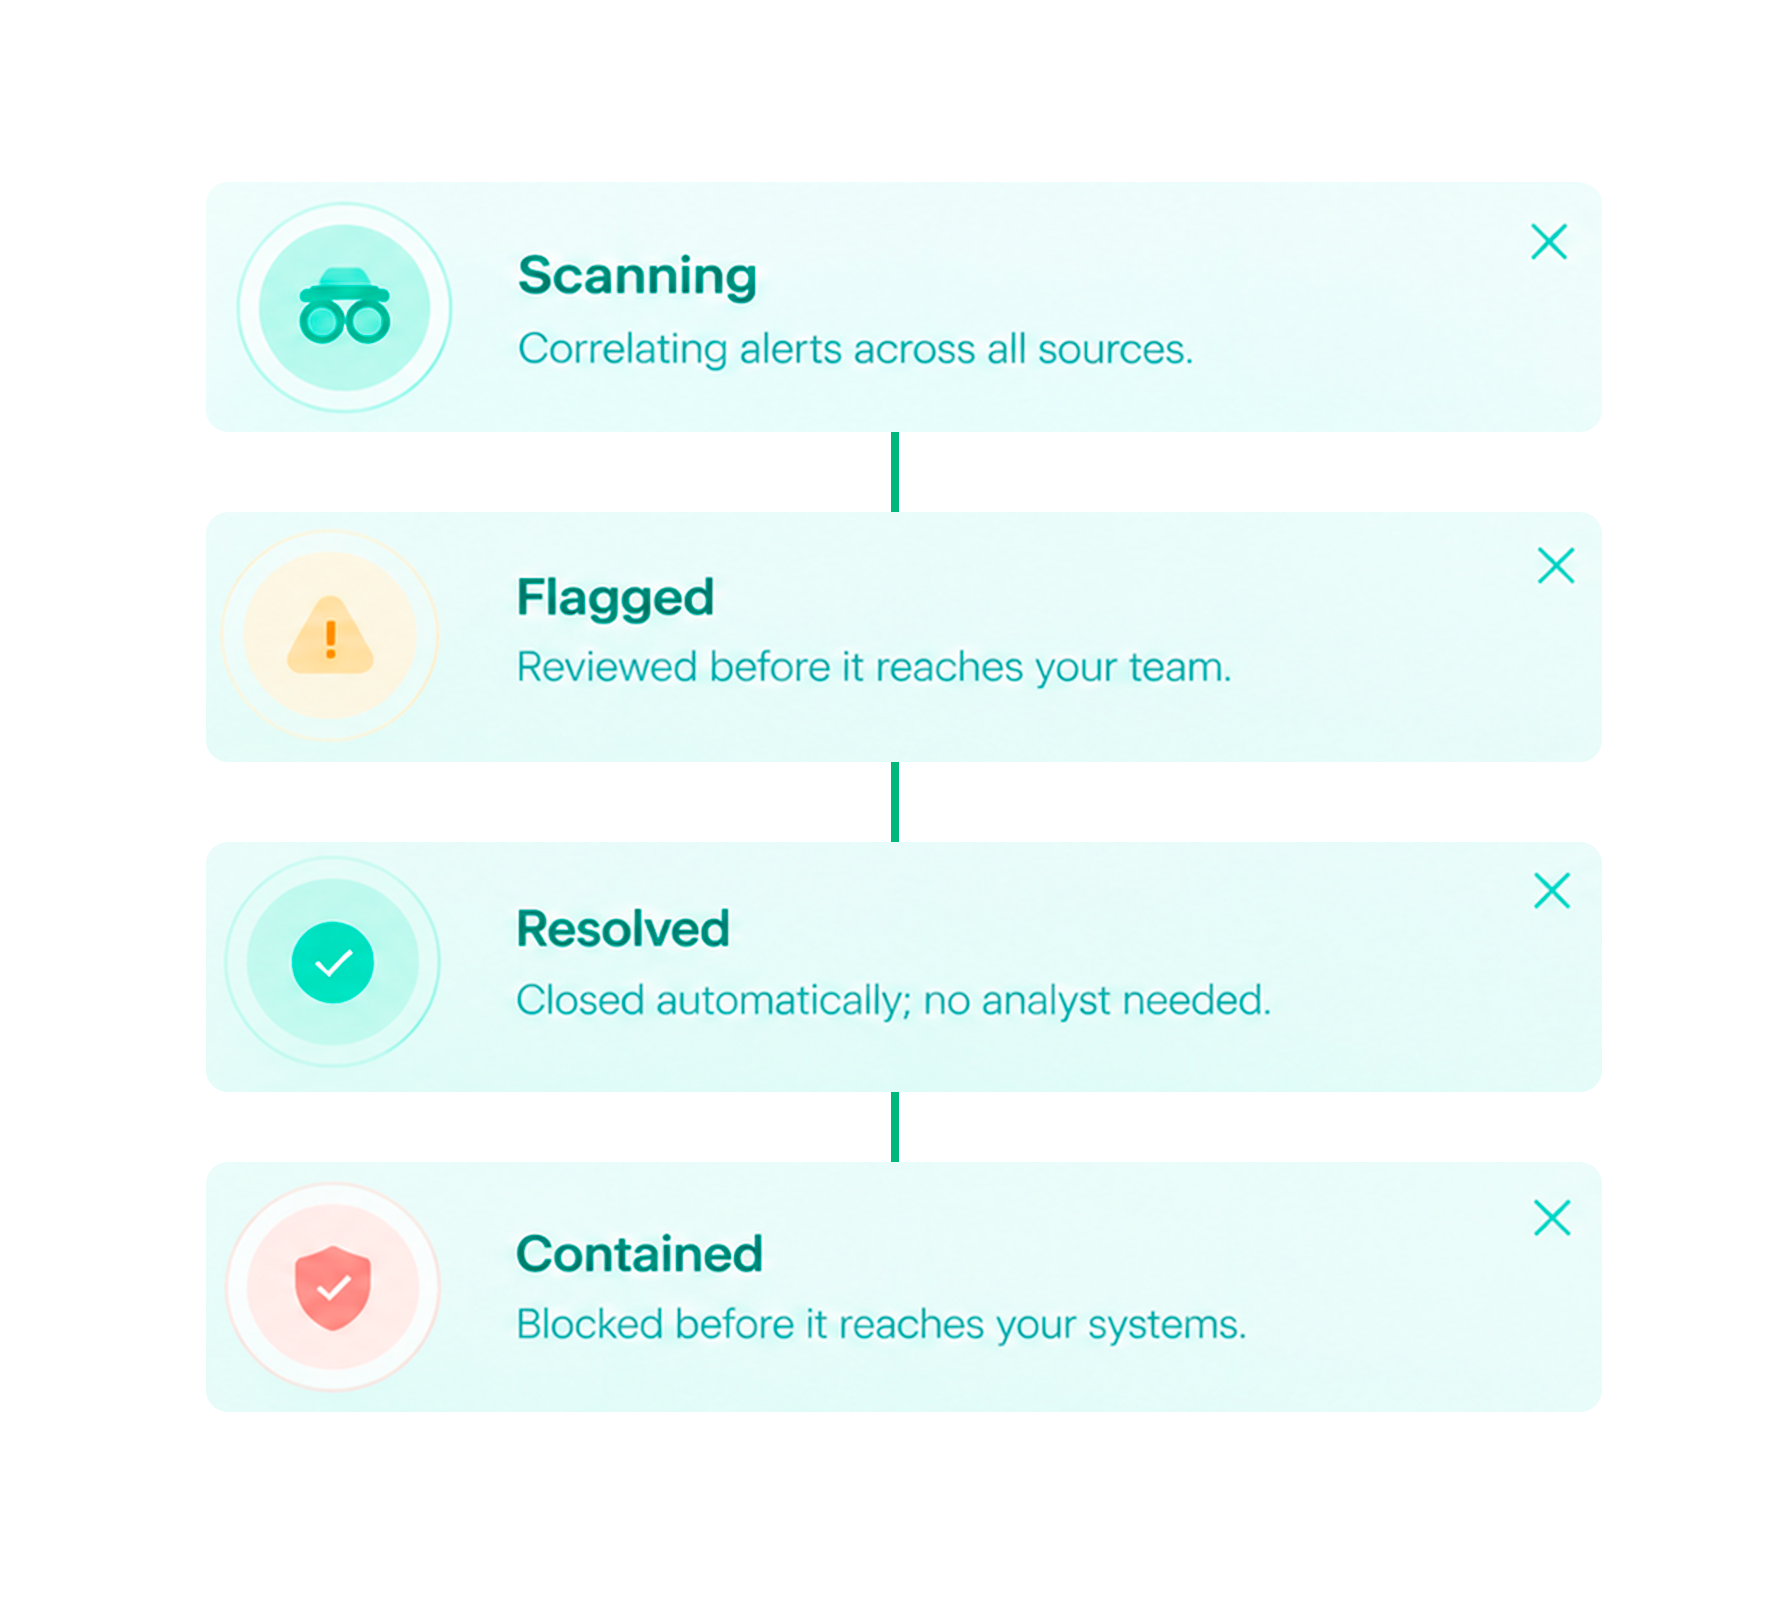
Your SIEM generates thousands of alerts. Our analysts triage every one before it reaches you. Custom detection rules written for your environment, updated continuously. 24/7 coverage by the same team that onboarded you.
in our SIEM
you see them
P1 incidents
included, no retainer
How it works
Every SIEM deployment starts fresh . Here's what that looks like.

Discovery & log connection
Your analyst reviews your environment and delivers a detection strategy before you sign. Every log source, endpoints, network, cloud, identity, SaaS, is connected and validated before detection work begins.
Custom detection rules
Every rule is mapped to MITRE ATT&CK and built from your stack, covering lateral movement, privilege escalation, and anomalous authentication from day one. Rules update continuously against active CVEs and emerging TTPs.

24/7 alert triage
Every alert is reviewed by a human analyst on shift. Confirmed findings arrive by email with severity and recommended action. Anything urgent gets a direct call to your consistent contact, not a queue.

Tuning & compliance evidence
Rules are tuned as your environment and the threat landscape change, with no quota on new releases. Compliance evidence is exported continuously in the format your framework requires.
How we stay accountable
You always know who is watching and what they are seeing.

CX Manager
Owns the relationship, runs on-demand executive reviews, escalation path for any service issue.

Technical Account Manager
Owns the detection program, runs monthly operational reviews, tracks security maturity over time.

SOC Analyst(s)
Work your environment day-to-day, writing and maintaining detection rules, running alert triage.

Threat Hunter
Builds proactive detection against emerging TTPs, shared across the full customer base.

Escalations
Analyst name, finding, severity, recommended action, delivered by email, direct call for anything urgent.

Monthly review
60 min with TAM. Detection performance, alert trends, rule changes, recommendations.

On-Demand EBR
60 min with CX Manager and TAM to review posture, coverage, and priorities. You set the cadence.

Ad hoc access
TAM via Slack or email during business hours. SOC via phone or portal 24/7 for active incidents.
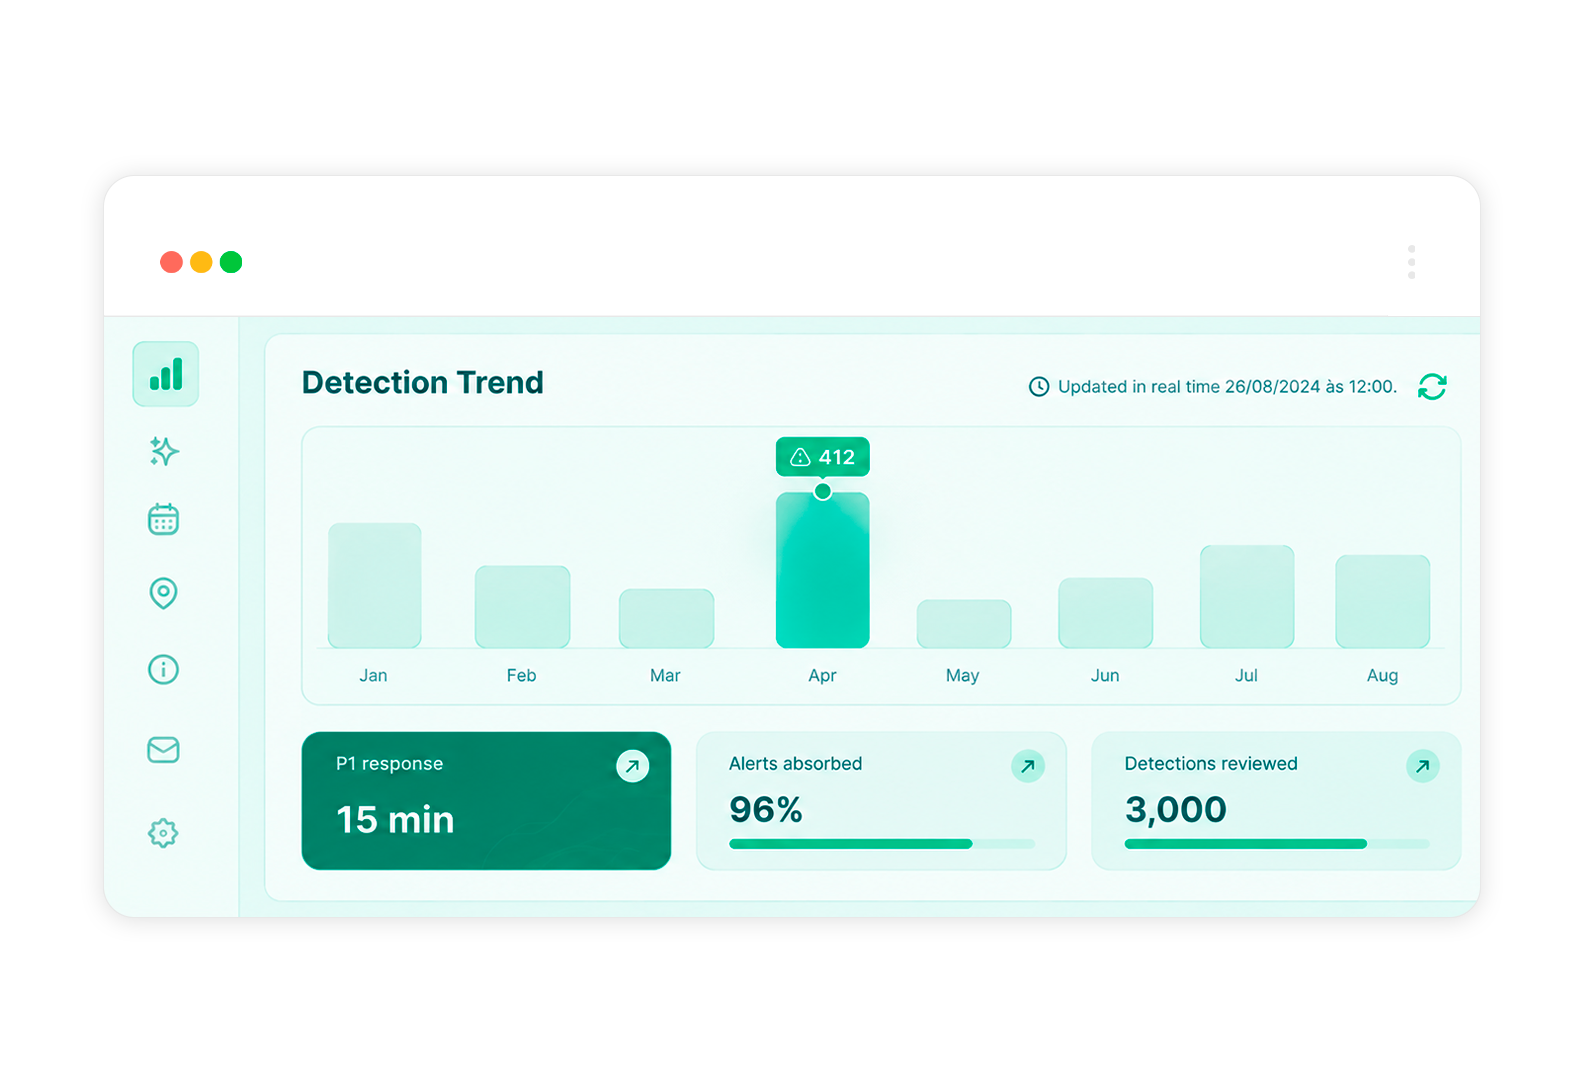
What the 60 minutes actually cover
Executive Business Review (EBR)
Structured as a working session with defined outcomes, not a reporting exercise. Covers:
How we use AI
AI handles the volume. Analysts handle the judgment.
(01)
What AI handles
Pre-screening and correlating alerts, so analysts spend less time on obvious noise.
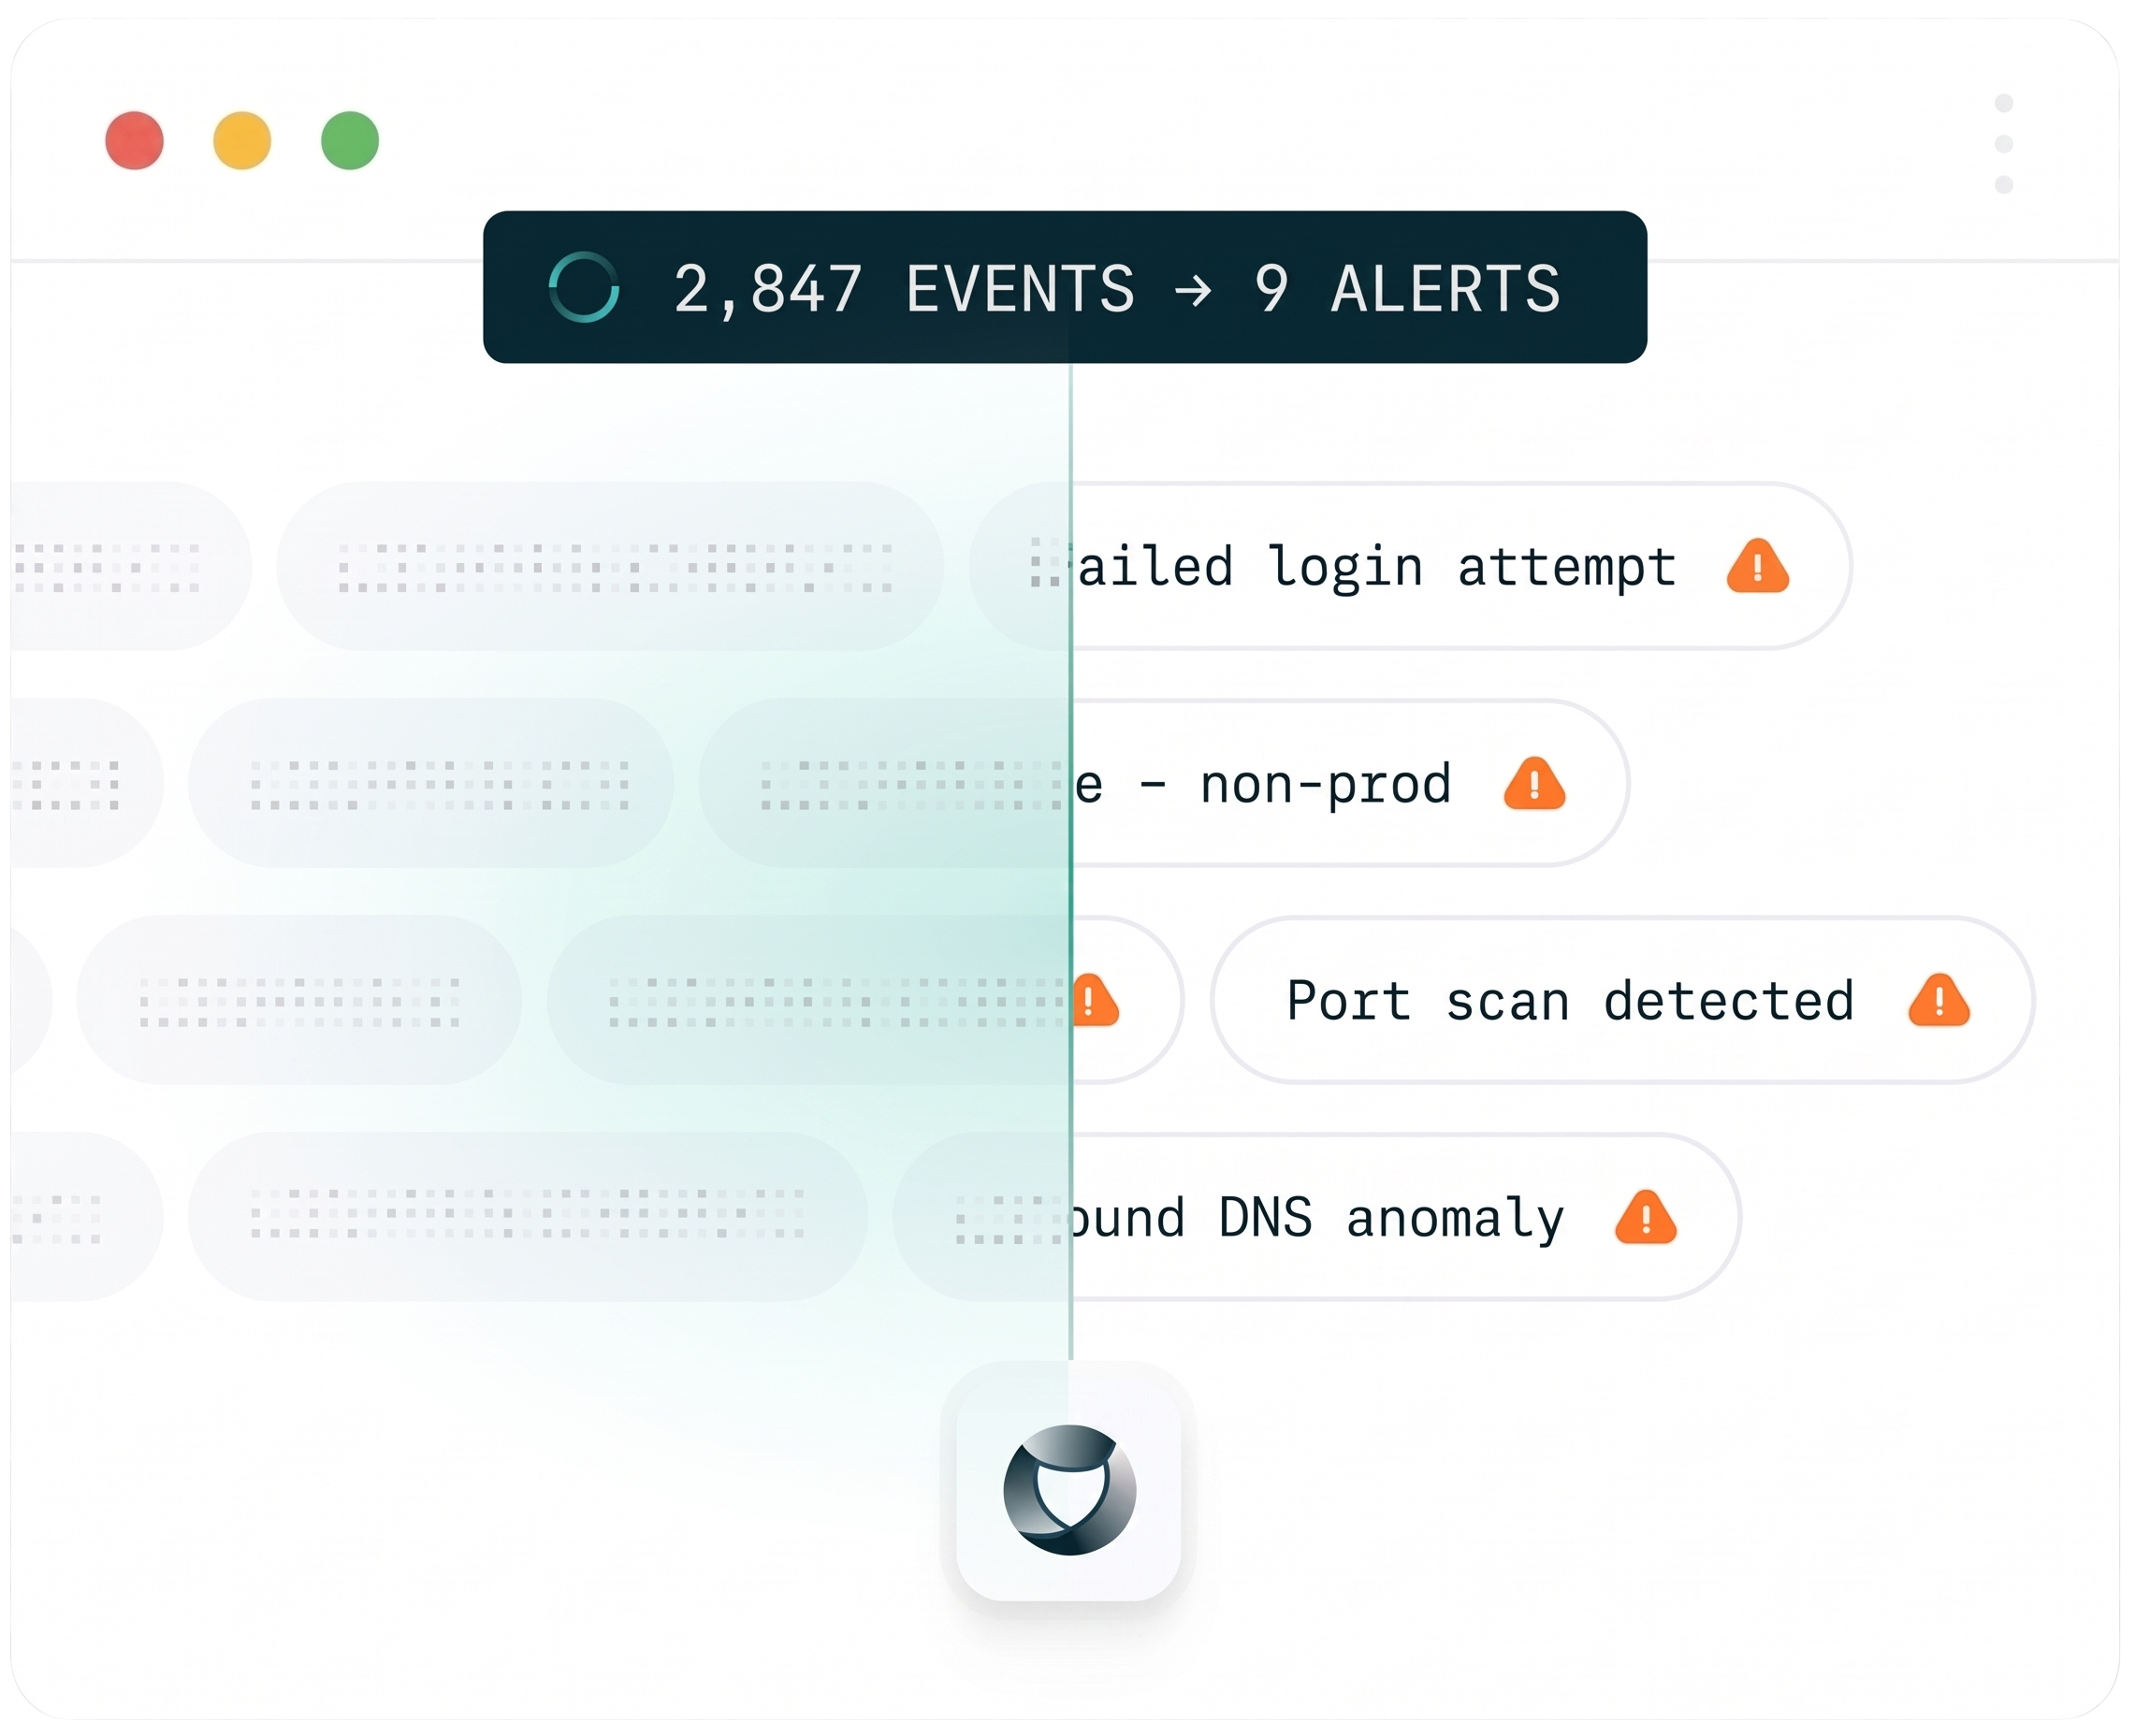
(02)
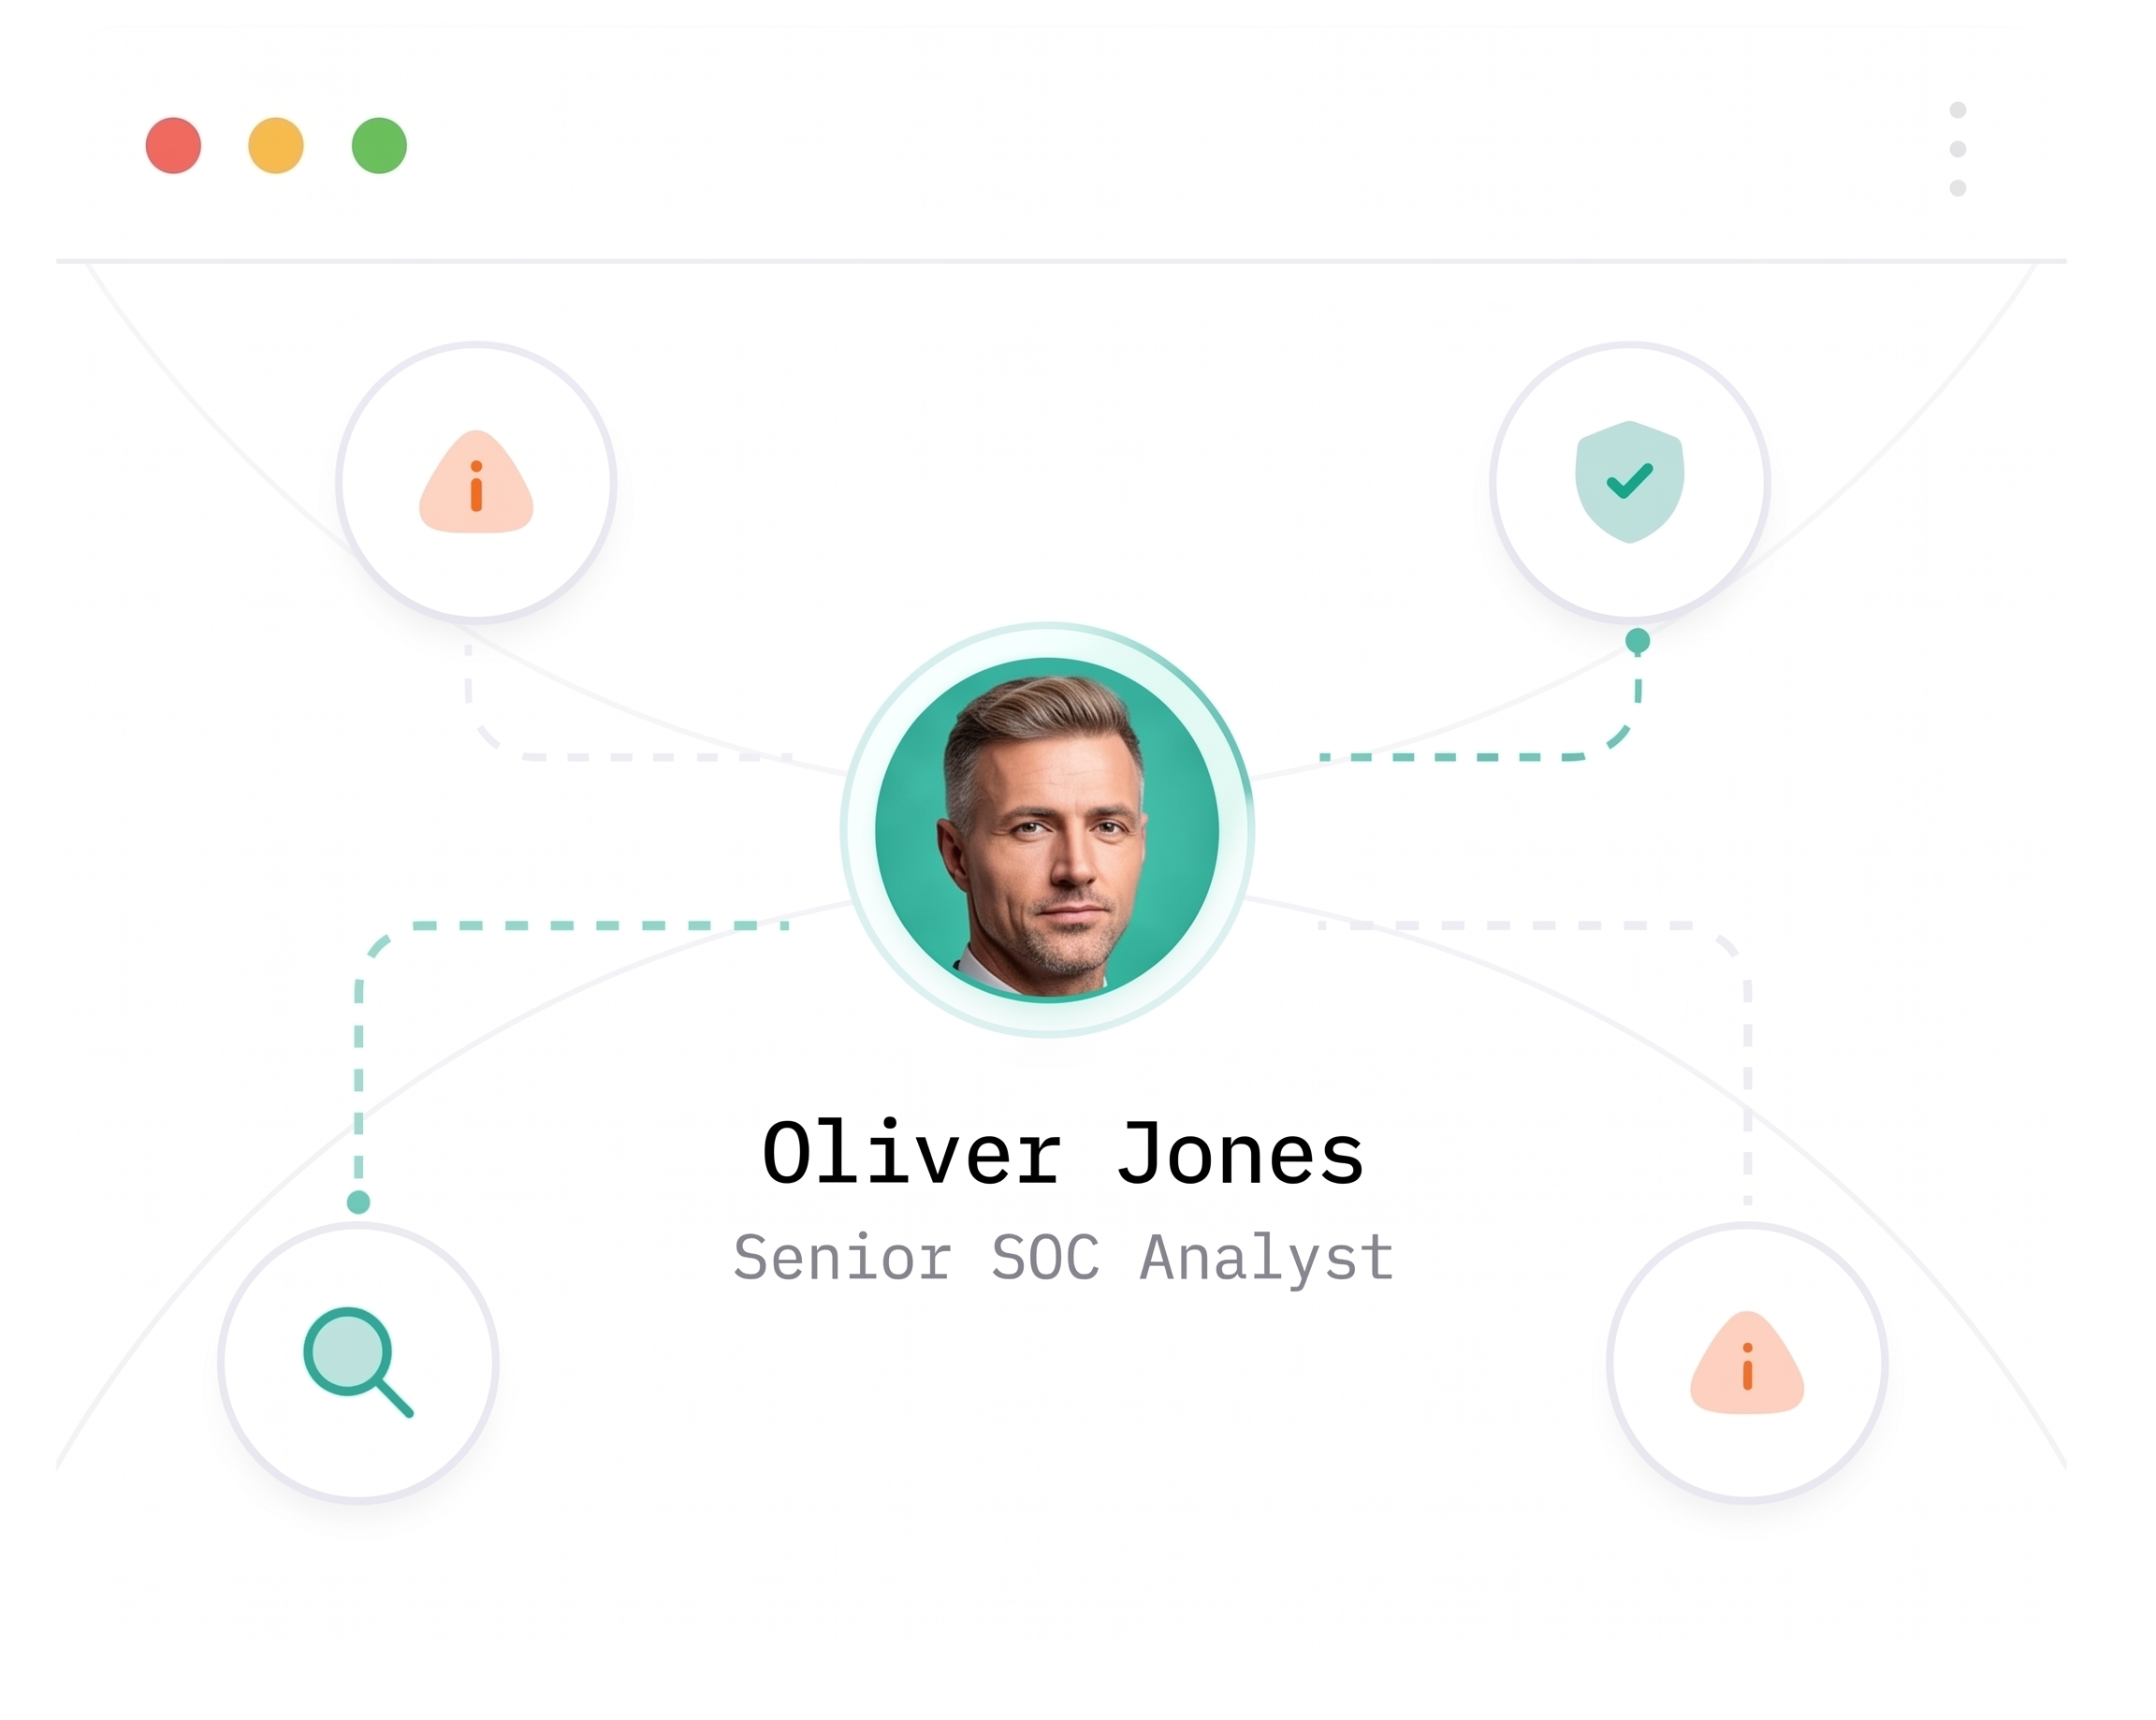
What AI does not do
AI doesn't decide escalations. A person reviews every alert. AI handles volume, analysts handle accountability.
Why this matters
SIEM is not a product.
Here's what running it changes.

Alert fatigue, eliminated
Every alert triaged by a human before it reaches you. Closed alerts include full analyst documentation. Nothing disappears into a black box.

Compliance evidence, produced continuously
Evidence built against your specific framework from day one. When your QSA arrives, the package is ready. When your insurer asks for documentation, it exists.

Environment-Aware Coverage
A ruleset built for your stack, tuned against your baseline behavior, updated as your infrastructure changes. Coverage that compounds over time.

120+ days of IT time returned
Alert triage, rule management, compliance reporting, handled. Your internal team gets 120+ days back each year to focus on the work they were hired to do.
How is OneAxiom priced?
Flat-rate, predictable pricing. No log-volume surprises and no separate IR retainer for the first 10 hours each month. You can see the model on our pricing page before you ever talk to sales.
How long does onboarding take?
Most customers are fully onboarded within a few weeks, depending on environment complexity.
Do you replace our internal IT or security team?
No, we work alongside your team as a consistent extension of it, not a replacement.
What tools do we need to buy first?
None. OneAxiom is built to work with your existing stack wherever possible.
What happens during an incident?
Your accountable team leads response immediately, with IR included in your plan.
Got questions
Frequently asked
and answered
Book a 30 min call
No commitment yet. We'll walk through your environment and see if there's a fit.